

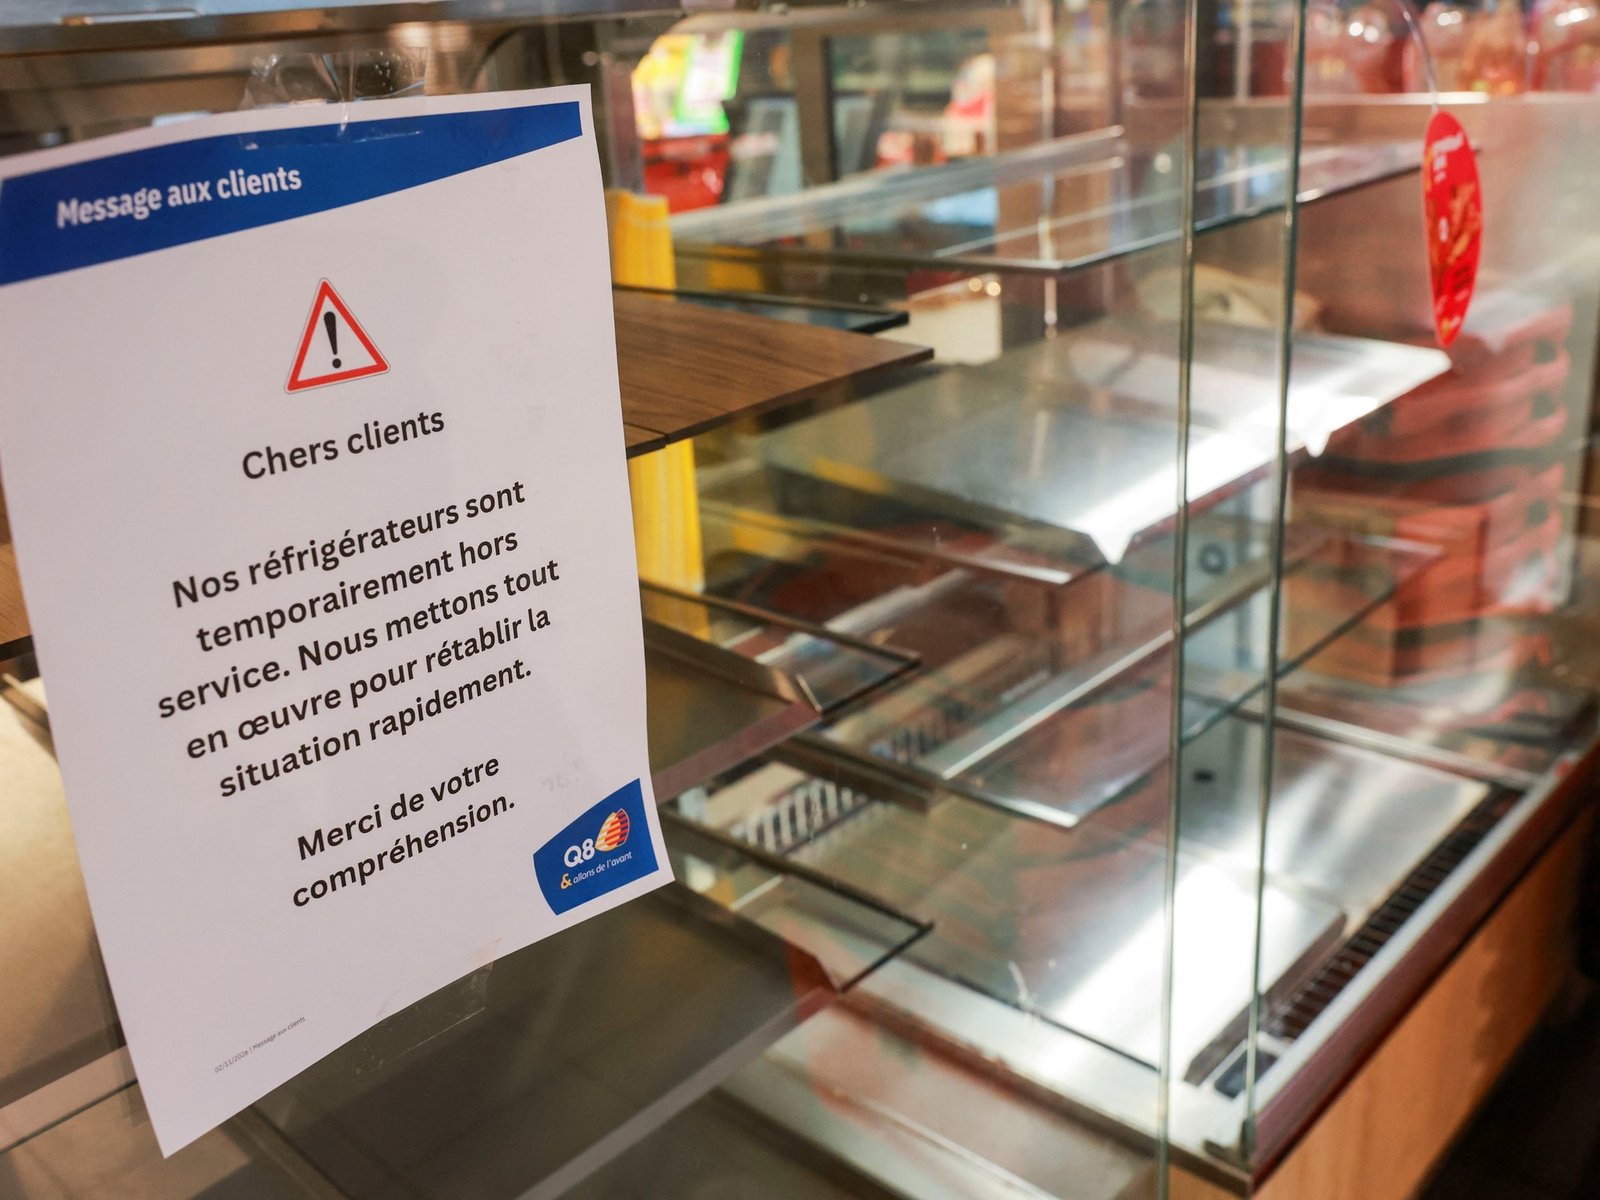
A coordinated wave of cyberattacks hit grocery store refrigeration systems across Belgium, Luxembourg, Estonia, Ireland, the Netherlands, and Sweden, forcing thousands of units into remote defrost mode and raising internal temperatures to 50 degrees Celsius or higher. The nocturnal assault ruined tons of meat, dairy, and frozen goods, mirroring an October 12 incident across 700 French supermarkets.
Operational Takeaways for Retail Logistics
- Centralized industrial refrigeration controllers remain a primary vector for supply chain sabotage across Europe.
- Remote management by specialized third-party vendors has inadvertently expanded the attack surface for major retail chains.
- Unlike historical ransomware incidents targeting checkout terminals, these operations focus strictly on physical asset destruction and inventory spoilage.
Industrial Refrigeration Vulnerabilities Surface Across European Retailers
The coordinated digital intrusion struck during the transition between Sunday and Monday, targeting core refrigeration infrastructures in multiple European nations. In Belgium, major chains including Carrefour and Delhaize absorbed the heaviest disruptions. Delhaize confirmed that its refrigeration systems are managed remotely by specialized third-party providers, with technical partner Sabcobel identifying the anomaly as an intentional cyberattack from the outset.
Sweden experienced parallel disruptions when employees at ICA stores arrived for early-morning shifts to find refrigeration units registering temperatures up to 50 degrees Celsius. According to corporate communications, the intrusion occurred at 02:00 local time, remaining undetected until morning store openings rendered the perishable inventory unsalvageable. In Ireland, 13 of the 223 supermarkets operated by SuperValu reported similar failures, while Estonian security firm Kitman Coldtech confirmed that unauthorized code successfully altered industrial temperature regulators to their maximum thermal limit.
Investigators Trace Digital Footprints Back to French Precedents
European authorities are coordinating their investigations with French officials, where the Paris Prosecutor’s office and specialized cybercrime units have been probing a larger October 12 incident involving more than 700 French supermarkets. During those earlier events, refrigeration units saw temperatures shift from -27 degrees Celsius to 50 degrees Celsius, with select systems experiencing physical fires. Dutch public broadcaster NOS reported at least 17 affected businesses in the Netherlands, encompassing both supermarkets and independent butcher shops.
UPDATE: Yes, I had to make another update. Upon further research, the total is now 12 countries affected by the European refrigeration cyberattack.🇸🇪 Sweden🇧🇪 Belgium🇱🇺 Luxembourg🇪🇪 Estonia🇮🇪 Ireland🇳🇱 Netherlands🇫🇮 Finland🇩🇰 Denmark🇮🇹 Italy🇷🇴 Romania🇩🇪 Germany🇵🇹… https://t.co/FnAz3ZSyJJ
Industry analysts point to systemic vulnerabilities in centralized industrial oversight. Supermarkets rely heavily on automated remote monitoring controllers to manage temperatures, schedule defrost cycles, and track energy consumption. Industrial cybersecurity firm Claroty previously identified vulnerabilities in a widely deployed family of remote controllers, specifically the Danfoss AK-SM 800A units, detecting 2,765 exposed devices. Following the October 12 attacks in France, Danish manufacturer Danfoss advised clients to disconnect refrigeration units from the public internet and restrict access to secure internal networks. However, technical indicators from the recent Belgian incidents suggest the compromised hardware utilized alternative controller architectures.
Contasting Past Digital Disruption Against Physical Inventory Destruction
Current retail disruptions mark a distinct tactical departure from historic cyber incidents. Previous high-profile attacks focused on financial extortion and transaction blockades. On July 2, 2021, a supply chain compromise originating at American software firm Kaseya forced Swedish cooperative Coop to shutter approximately 800 stores due to point-of-sale terminal failures. Similarly, British retailer Co-op absorbed nearly $125 million in losses during 2025 following IT compromises that disrupted inventory management. Fellow UK merchant Marks & Spencer sustained over $350 million in damages from an e-commerce infrastructure breach during the same fiscal cycle. Unlike those data-centric events, the current European refrigeration attacks have yielded no financial ransom demands and no official claim of responsibility from any domestic or foreign group.
| Incident Date | Affected Enterprise / Region | Primary Operational Impact |
|---|---|---|
| July 2, 2021 | Coop (Sweden) | 800 stores closed due to point-of-sale terminal outages via Kaseya software breach. |
| 2025 Fiscal Year | Co-op (United Kingdom) | Generated nearly $125 million in losses from inventory and management system disruptions. |
As cybersecurity authorities continue cross-border forensic analysis, the central question remains unanswered: without financial extortion demands or claims of responsibility, investigators have yet to establish clear attribution or motive for the physical sabotage of Europe’s cold-chain logistics.
Disclaimer: The information provided in this article is for educational and informational purposes only and does not constitute financial advice.
