
Despite firmware patches issued by SonicWall, threat actors continue to compromise unpatched or improperly configured systems by reusing pre-harvested credentials and hijacking multi-factor authentication protocols.
The Mechanics of CVE-2024-40766 and Ingress Vectors
Assigned a critical CVSS score of 9.3, CVE-2024-40766 stems from an improper access control flaw within the SonicOS management interface handler and SSLVPN services managed by the httpd daemon. When unauthenticated remote threat actors transmit crafted HTTP or HTTPS requests across wide-area networks targeting ports 443 or 4433, they can bypass authorization boundaries. This exploitation allows attackers to access runtime memory buffers containing plaintext or hashed credentials, extract system configurations, or trigger kernel panics and hardware watchdog resets that crash the firewall.
The vulnerability impacts multiple hardware generations running both legacy and modern firmware architectures.
| Hardware Generation | Model Families | Vulnerable Firmware | Patched Baseline |
|---|---|---|---|
| Gen 5 (Legacy) | SOHO | ≤ 5.9.2.14-12o | 5.9.2.14-13o (or WAN isolation) |
| Gen 6 | TZ series, NSA, SuperMassive | ≤ 6.5.4.14-109n | 6.5.4.14-110n / 6.5.4.15-116n |
| Gen 7 | TZ (TZ270–TZ670), NSA (2700–6700) | ≤ 7.0.1-5035 | SonicOS 7.3.0+ (or 7.0.1-5051 / 7.1.1-7051) |
Why Firmware Patches Alone Fail Against Akira Affiliates
Deploying official patches does not automatically stop intrusions. Forensic investigations conducted by incident response teams reveal that organizations are falling victim to recurring attacks even after updating their appliance firmware. Threat actors bypass perimeters by exploiting three compounding configuration weaknesses.
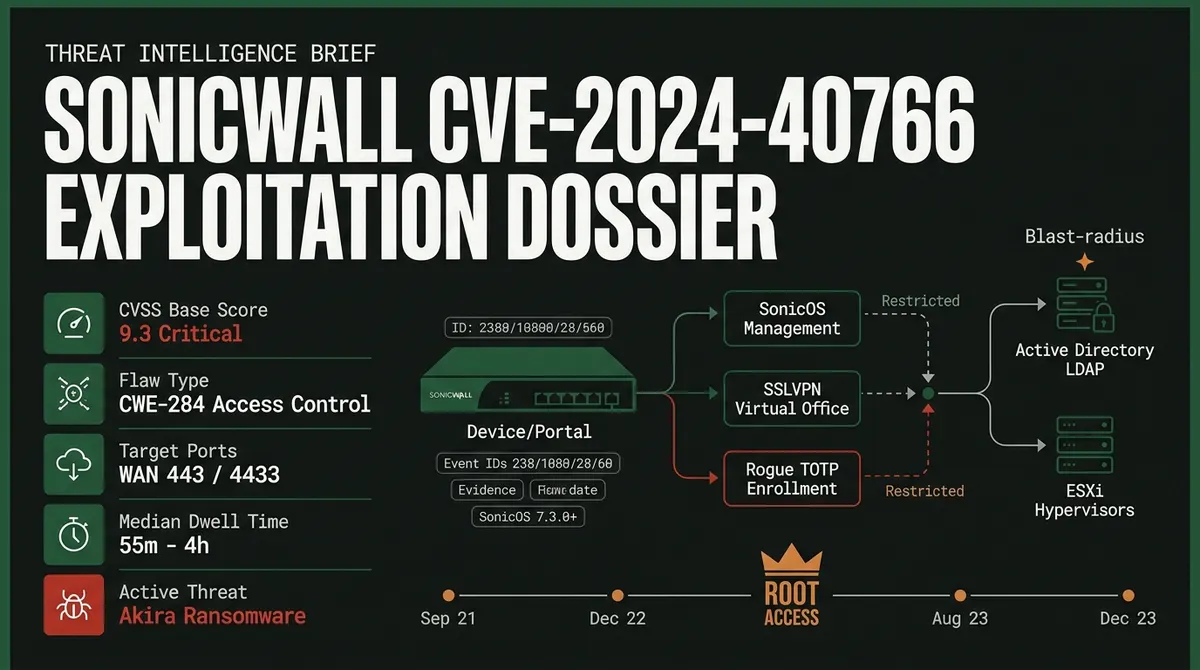
First, attackers leverage secrets harvested from appliance memory prior to patching, credentials exposed in unencrypted backup preference files, and legacy local accounts preserved during hardware migrations from Gen 6 to Gen 7 units. Second, threat actors exploit the external Virtual Office Portal hosted on default ports. If an account has multi-factor authentication enabled globally but has not completed initial setup, or if an administrator resets MFA without forcing immediate internal enrollment, SonicOS presents the time-based one-time password registration QR code upon the first successful password login. Akira affiliates intercept this prompt to bind a rogue authenticator app to the compromised account, granting them persistent, legitimate access to corporate networks.
Security agencies have mobilized in response to the renewed campaign. The Australian Cyber Security Centre (ACSC) issued an urgent advisory highlighting the rise in domestic exploitation.
SonicWall Clarifications and Enterprise Mitigation Requirements
Following a spike in attacks that initially sparked industry confusion and speculation regarding a potential zero-day exploit, SonicWall moved quickly to clarify the threat landscape. The vendor stated it had high confidence that the recent SSLVPN activity was not connected to a zero-day vulnerability, noting a significant correlation with threat activity related to CVE-2024-40766. Last month alone, SonicWall investigated up to 40 security incidents tied directly to this exploitation vector.
To eliminate unauthorized access risks, SonicWall and cybersecurity analysts emphasize that firmware updates must be paired with rigorous administrative remediation steps. Organizations running vulnerable appliances must update firmware to version 7.3.0 or later, rotate all passwords for locally managed SSLVPN accounts immediately, enforce multi-factor authentication across every user profile, restrict Virtual Office Portal access exclusively to trusted or internal networks, and review permissions associated with SSLVPN default groups to prevent privilege escalation.
