
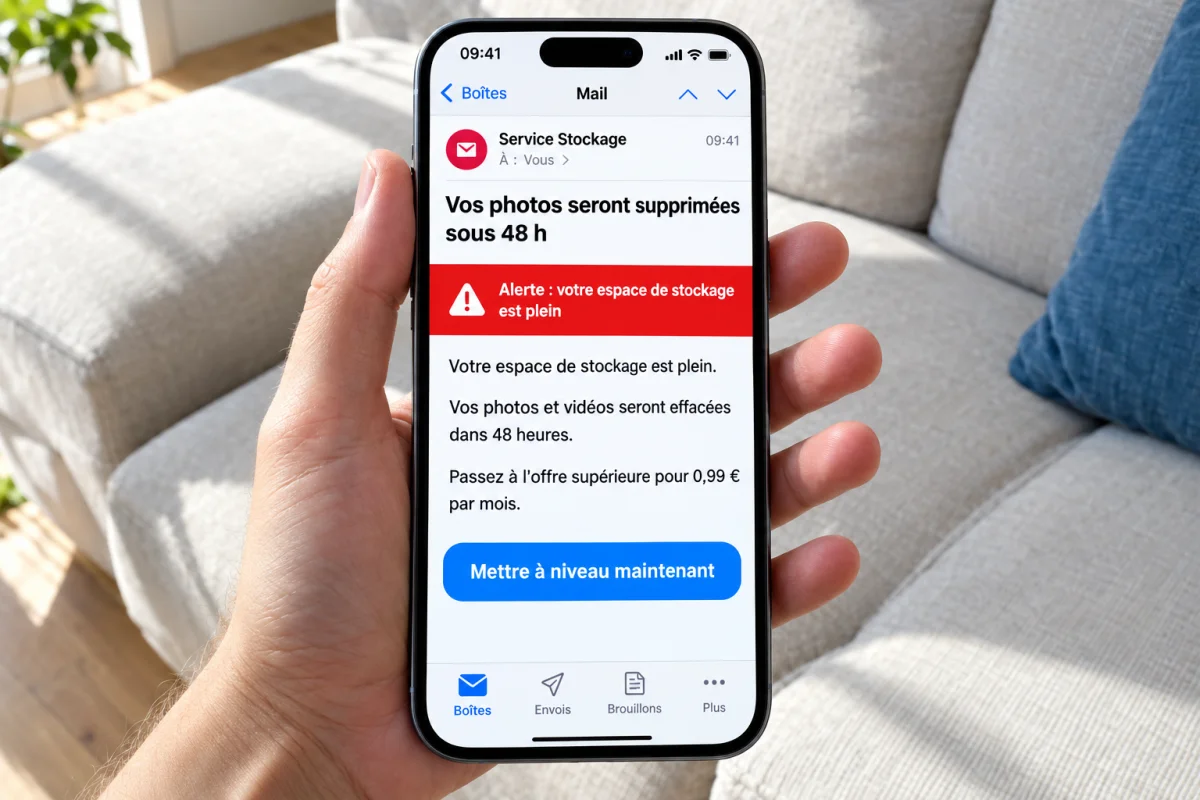
An alarming SMS or email warning that an iCloud storage quota is completely full and threatening total photo deletion within 24 to 48 hours unless a 0.99 € iCloud+ fee is paid immediately is actually a phishing trap, as selectra.info reported.
The 48-Hour Deletion Threat
The ultimatum itself exposes the scam. Exceeding cloud capacity triggers no sudden, overnight disappearance of personal libraries.
Apple terms state that hitting the storage ceiling stops device backups, halts new photo uploads to iCloud Photos, pauses iCloud Drive synchronization, and disables incoming or outgoing mail on an iCloud address. Apple terms updated on September 14, 2026, allow data removal past the quota limit only after a mandatory 30-day notice period. A demand warning of deletion in 24 or 48 hours completely contradicts official platform policy.
Google Storage Quota Realities
Google maintains a similarly measured timeline for accounts running over their capacity limits. Google can delete content across Gmail, Google Photos, Drive, and Android backups after at least two years of continuous quota excess, issuing email warnings and device notifications at least three months prior.
Immediate consequences remain strictly functional rather than destructive. Gmail stops sending and receiving messages, Drive rejects new file uploads, and Google Photos halts syncing right away. Losing data overnight is a myth engineered entirely by scammers.
Detecting the Phishing Tactics
Official alerts regarding storage exist, which makes the manufactured ultimatum the primary red flag. Apple identifies several specific indicators of phishing attacks designed to steal credential data.
- The sender address fails to match official Apple domains.
- The embedded link directs users away from authentic Apple infrastructure.
- The message demands credit card numbers or explicit passwords.
- It asks for multi-factor authentication codes or payment via retail gift cards.
Security vendor Malwarebytes documented a recurring campaign running through April 2026 that issued multiple rapid-fire warnings before citing a fixed execution date within two days, pushing a 99-cent iCloud+ tier designed purely to harvest payment instrument data.
Verifying Storage Safely
Checking actual account status requires bypassing incoming links entirely. On an iPhone, users navigate to Réglages > [votre nom] > iCloud to inspect the real utilization gauge. Google One provides identical telemetry.
If a storage gauge truly registers as full, pruning files requires caution. When an account exceeds its quota, deleted photos and videos vanish instantly without passing through the Recently Deleted album. Users must verify local copies exist elsewhere before purging files.
Immediate Response Protocols
Anyone who falls for the trap and submits payment details must contact their bank immediately to issue a card block and subsequently rotate account passwords. Cybermalveillance.gouv.fr outlines precise reporting pathways for digital fraud.
Fraudulent Apple emails route to [email protected], while SMS threats require a screenshot sent to the same destination. Fraudulent emails also process through Signal Spam, SMS scams route to 33 700 via the French national reporting service, and rogue domains go to Phishing Initiative.
Under article L133-18 of the French monetary and financial code, banks must reimburse unauthorized and reported transactions by the end of the next business day. Exceptions apply if the institution suspects gross negligence, codified under négligence grave, though the burden of proof rests entirely on the financial institution.
