
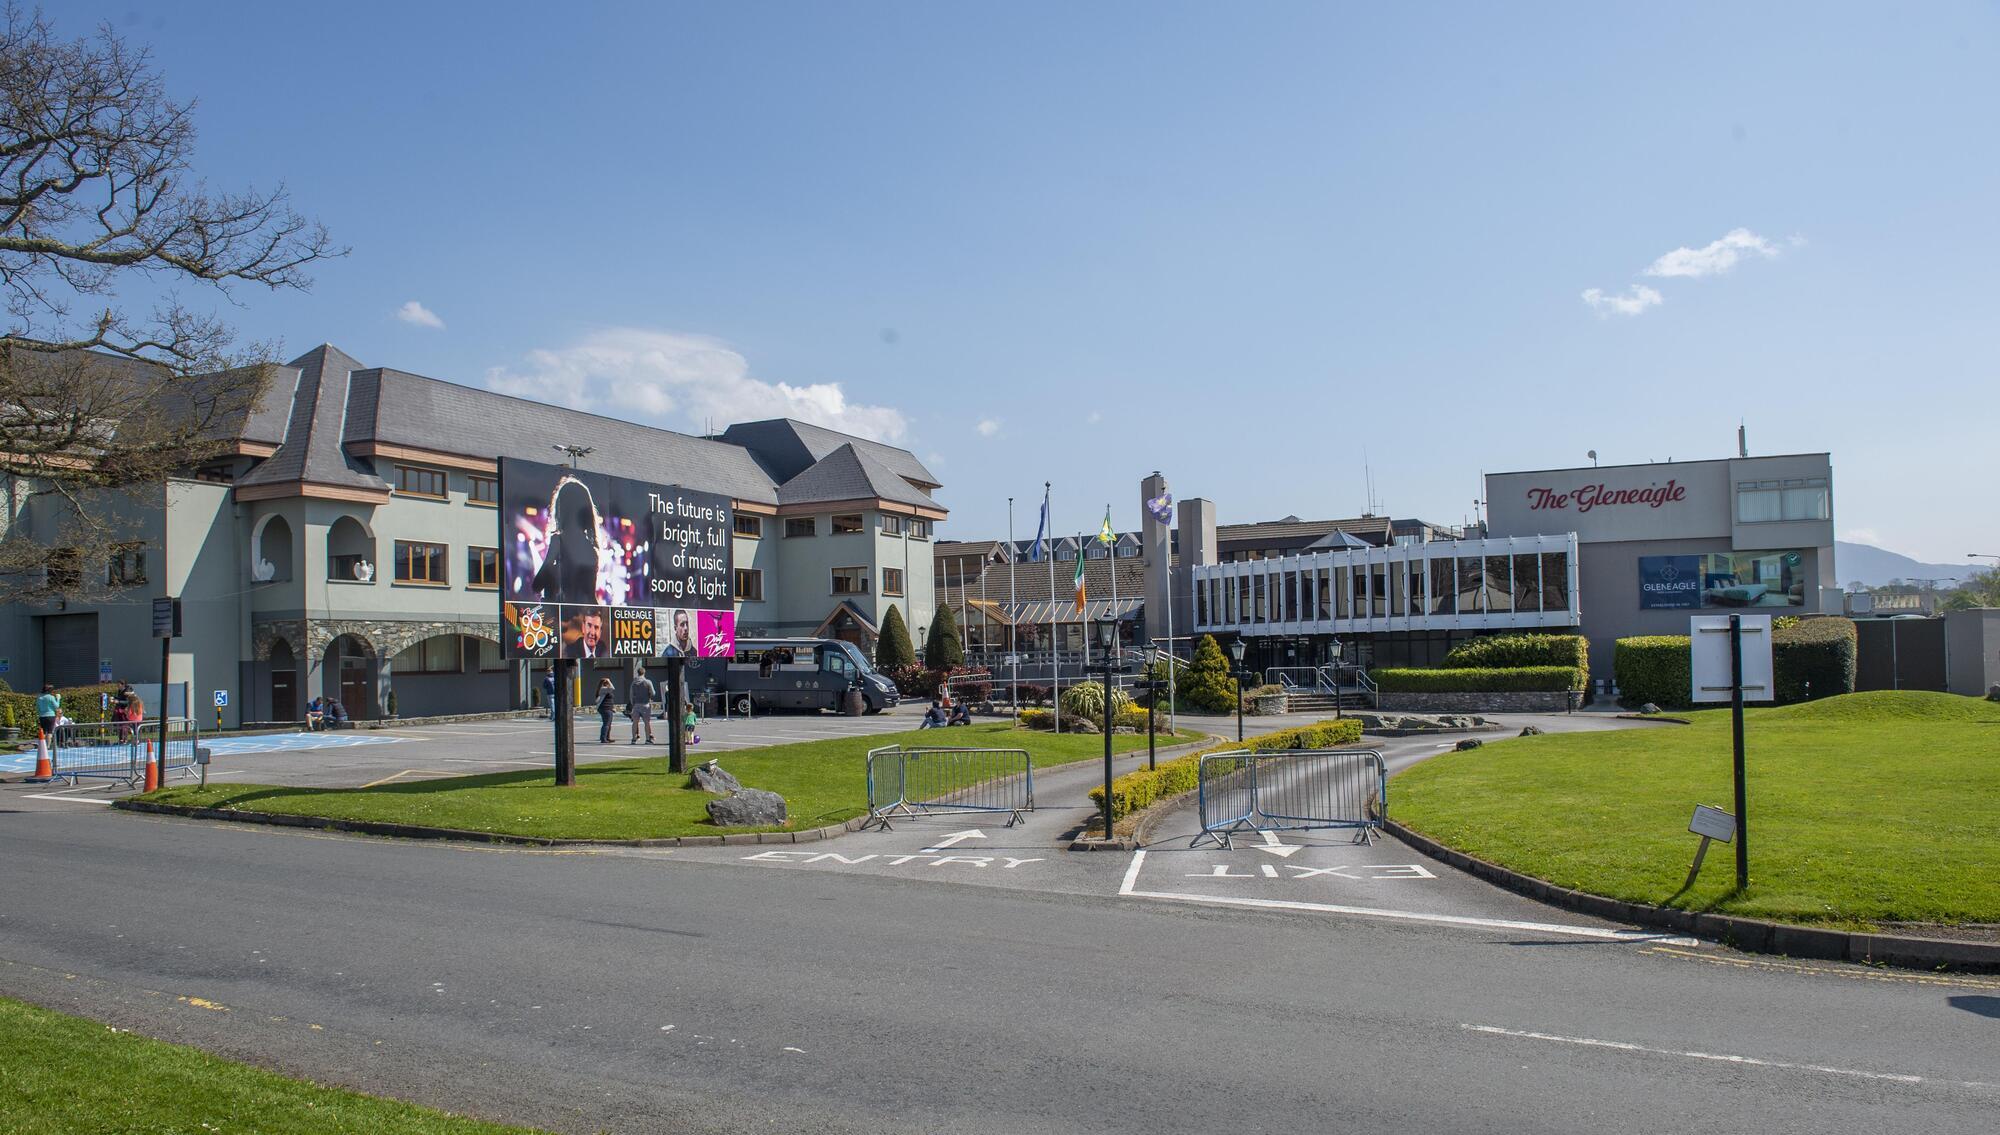
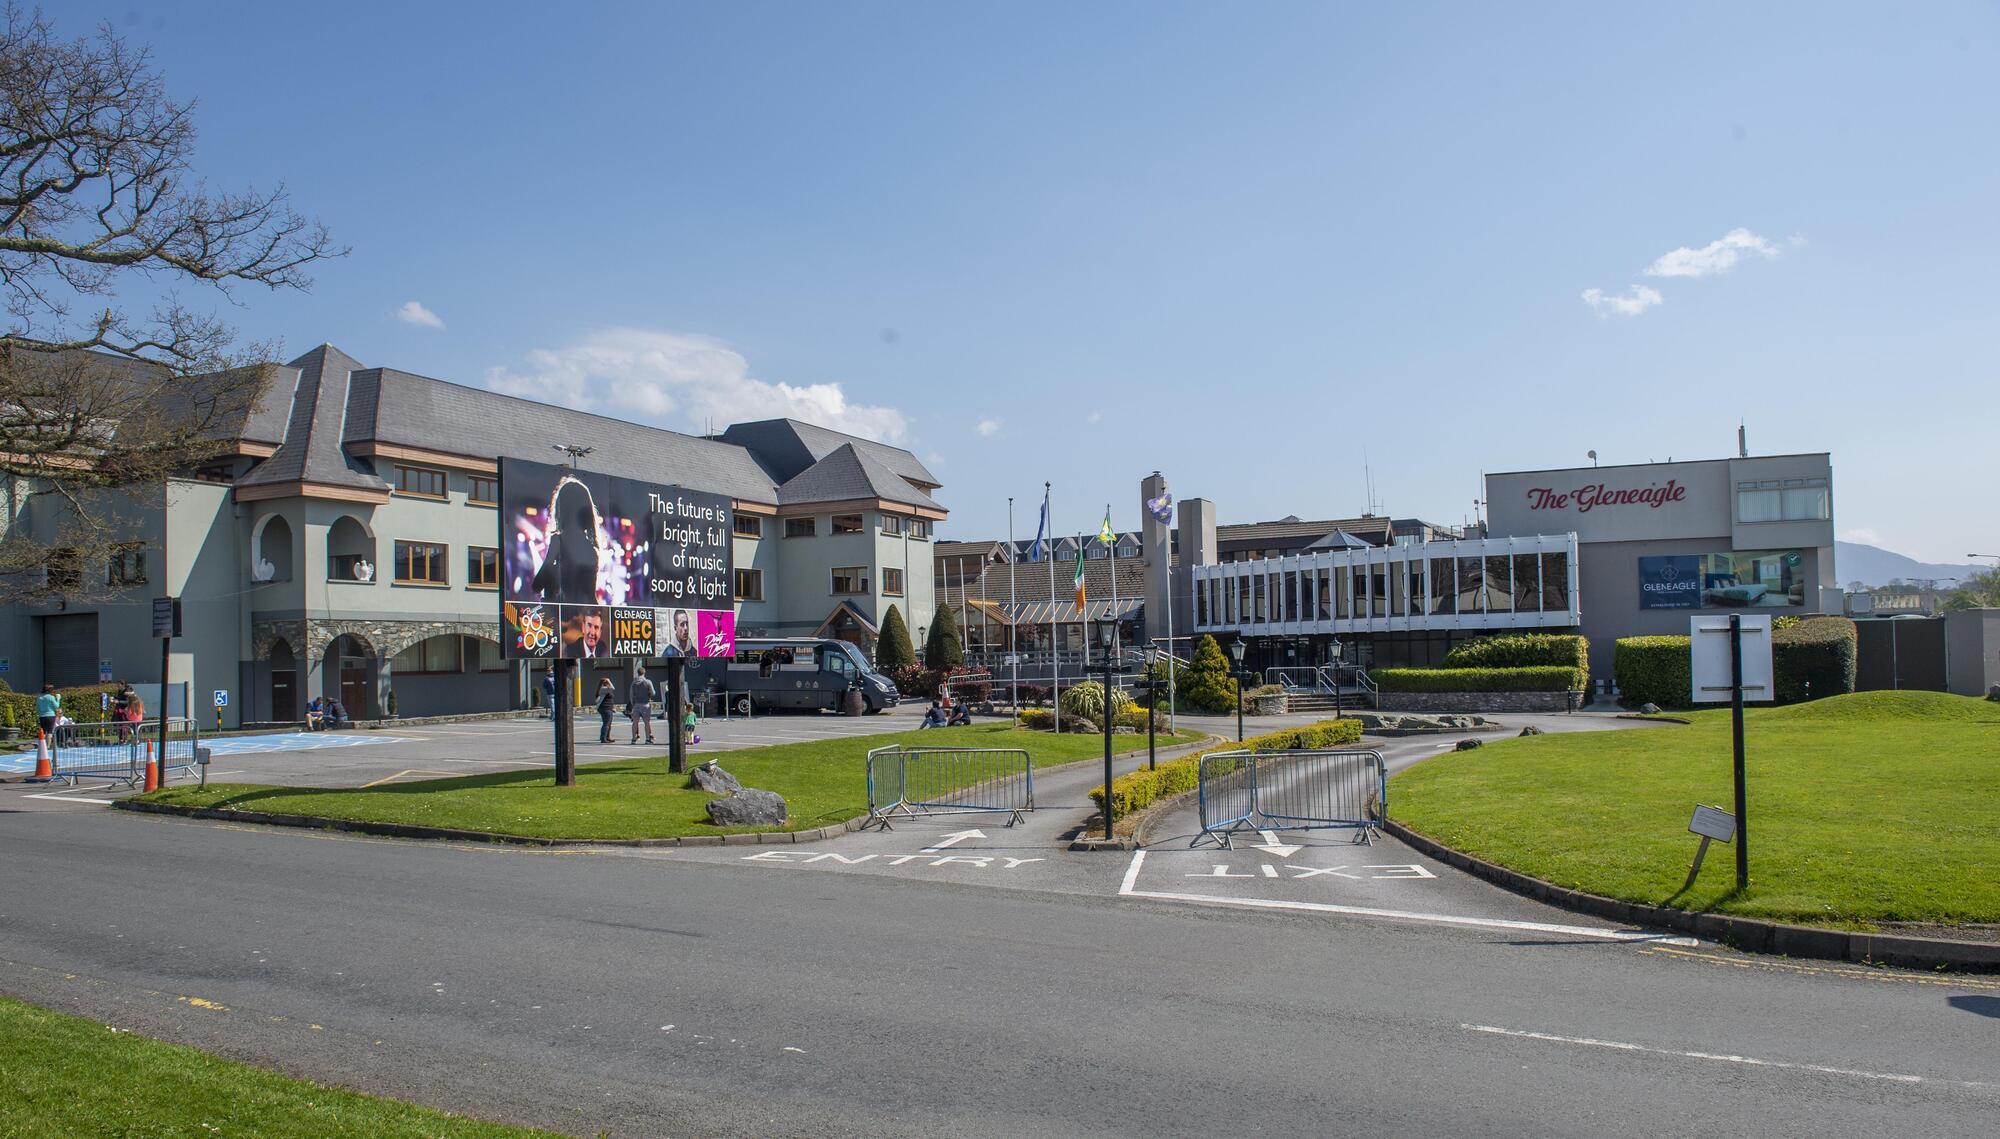
Guest reservation details were exposed in a security breach affecting a third-party booking engine provider used by Kerry’s Gleneagle Hotel, according to echo live.
The unauthorized access occurred on Sunday, November 15, when an outside party entered the administration system of the third-party booking engine. Before the provider blocked access and secured the infrastructure, the intruder is believed to have exported a file containing specific guest reservation records.
The security incident impacts reservations across the Gleneagle property in Killarney, including Hotel67 and the Gleneagle River Apartments, as reported by echo live. The exposed data fields were limited to names, email addresses, booking references, and guest arrival and departure times.
Financial records and authentication credentials remained untouched during the intrusion. Irish Examiner reported that no card payment details, bank details, residential addresses, telephone numbers, or passwords were accessed by the unauthorised party.
Booking Engine Provider Secures Systems and Notifies Regulators
The booking engine provider has secured its environment and launched a full investigation into the breach. Management at the property confirmed that the Data Protection Commission has been formally notified of the incident.
Property representatives said that all affected guests have been contacted as a precaution. Management advised those individuals to remain vigilant regarding unexpected communications requesting personal information or payment details.
Killarney's Gleneagle Hotel confirms guest data leaked in security breach https://t.co/4hBFre7xTF
“We can confirm that a security incident involving our third-party booking engine provider resulted in unauthorised access to certain guest reservation details. The incident relates to reservations for Gleneagle, including Hotel67 and Gleneagle River Apartments, which operate as part of the same property in Killarney.”
said a statement from the Gleneagle, issued on Tuesday.
The property also addressed the scope of the exposed information in its public communication.
“The information involved was limited to booking references, dates of stay, and the names and email addresses associated with those bookings. No residential addresses, telephone numbers, payment card details, bank details or passwords were involved,” the statement added.
Current checks indicate that the compromised data has not been leveraged for malicious activity. Irish Examiner said that property management confirmed there is no evidence to date that the information has been used fraudulently.
