
South Korean lifestyle platform Musinsa is preparing formal legal complaints with investigative agencies after bad actors used its corporate identity to orchestrate a sophisticated fake recruitment campaign targeting young job seekers, tv.edaily.co.kr reported.
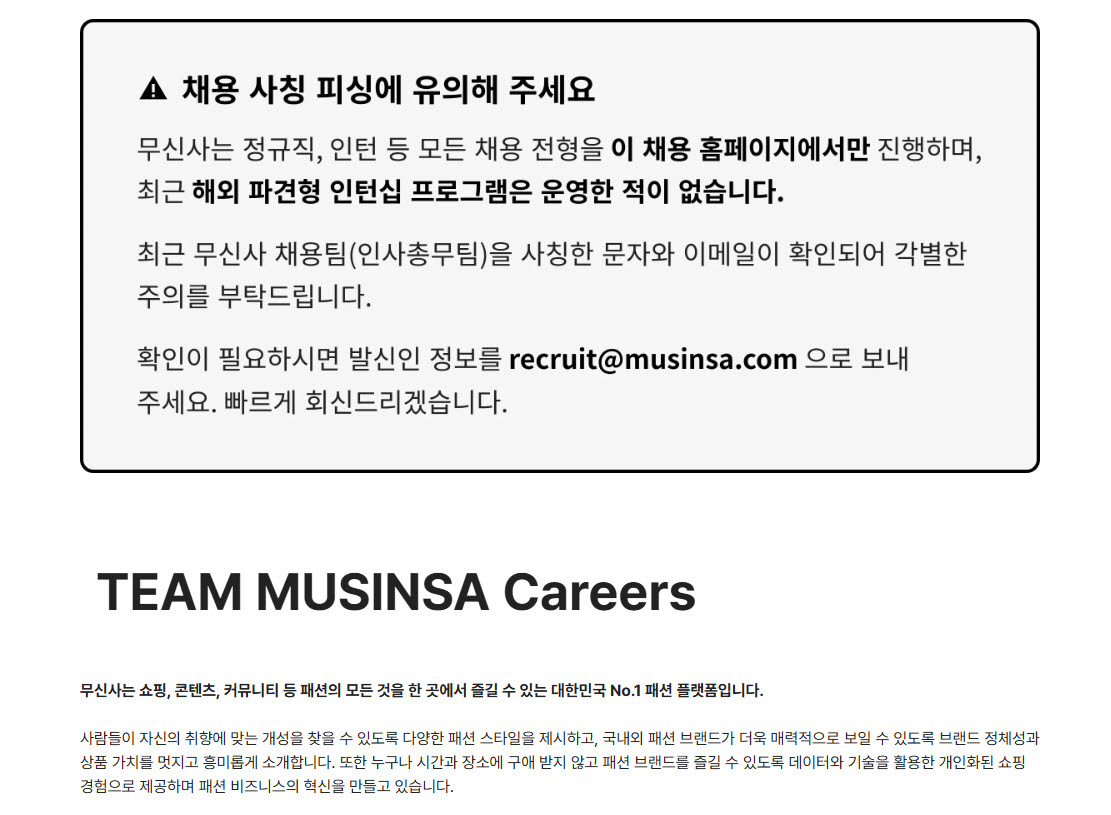
The fraudulent scheme went far beyond standard phishing emails. Unidentified perpetrators impersonated the “Musinsa Human Resources and General Affairs Team” to contact applicants directly via email and text message, offering fake marketing intern positions. The communications included detailed deployment plans requiring victims to report for work at a non-existent office in London, England. Musinsa confirmed that it maintains no such internal department, operates no European subsidiary, and runs no international dispatch internship programs.
How the Recruitment Fraud Unfolded
The deception relied heavily on familiarity with corporate hiring nomenclature. Normal recruitment at Musinsa runs exclusively through its official portal, “Musinsa Careers,” handling everything from initial application intake to final pass notifications. By bypassing this official infrastructure and conducting communications through direct messaging apps and external email addresses, the bad actors created a convincing facade of legitimacy.
Musinsa discovered the fraudulent activity on November 6 and posted an urgent warning notice on its official career portal by November 7. The company is actively working to identify individuals who received the fraudulent messages as well as the perpetrators behind the scheme. With a registered user base exceeding 16 million people—more than half of whom belong to the digital-native 2030 demographic—the platform proved to be an attractive target for bad actors looking to exploit young, career-minded job seekers.
| Target Company | Year of Incident | Method of Impersonation |
|---|---|---|
| Musinsa | 2026 | Fake marketing intern offers and London dispatch instructions |
| Starbucks Korea | 2024 | Phishing recruitment sites and remote-work deposit scams |
| Big Hit Music (HYBE) | 2024 | Fake recruitment texts promising daily pay for album reviews |
A Growing Trend Across High-Profile Brands
The incident at Musinsa mirrors a broader wave of corporate identity theft targeting major consumer brands in South Korea. Major consumer-facing businesses frequently find their names weaponized to exploit anxious job seekers.
Starbucks Korea encountered a similar ordeal in July 2024, when scammers used bogus recruitment websites and text messages to harvest personal information and demand upfront money transfers for remote-work part-time positions. In September 2024, fraudsters distributed fake recruitment text messages bearing the name of Big Hit Music, an affiliate of entertainment giant HYBE. Those messages promised daily wages for reviewing music and adjusting track rankings.
While Musinsa confirmed that no actual data breaches or financial losses have been identified among victims so far, the company is moving swiftly to prevent further exposure. Beyond updating its official career portal, the platform is rolling out warning banners across its main shopping application, official social media channels, and targeted text notifications sent to dormant account holders.
Company representatives emphasize that all legitimate hiring processes occur strictly within official domain boundaries. The upcoming filings with investigative authorities mark a transition from passive public notices to active legal deterrence against recurring corporate impersonation schemes.
