

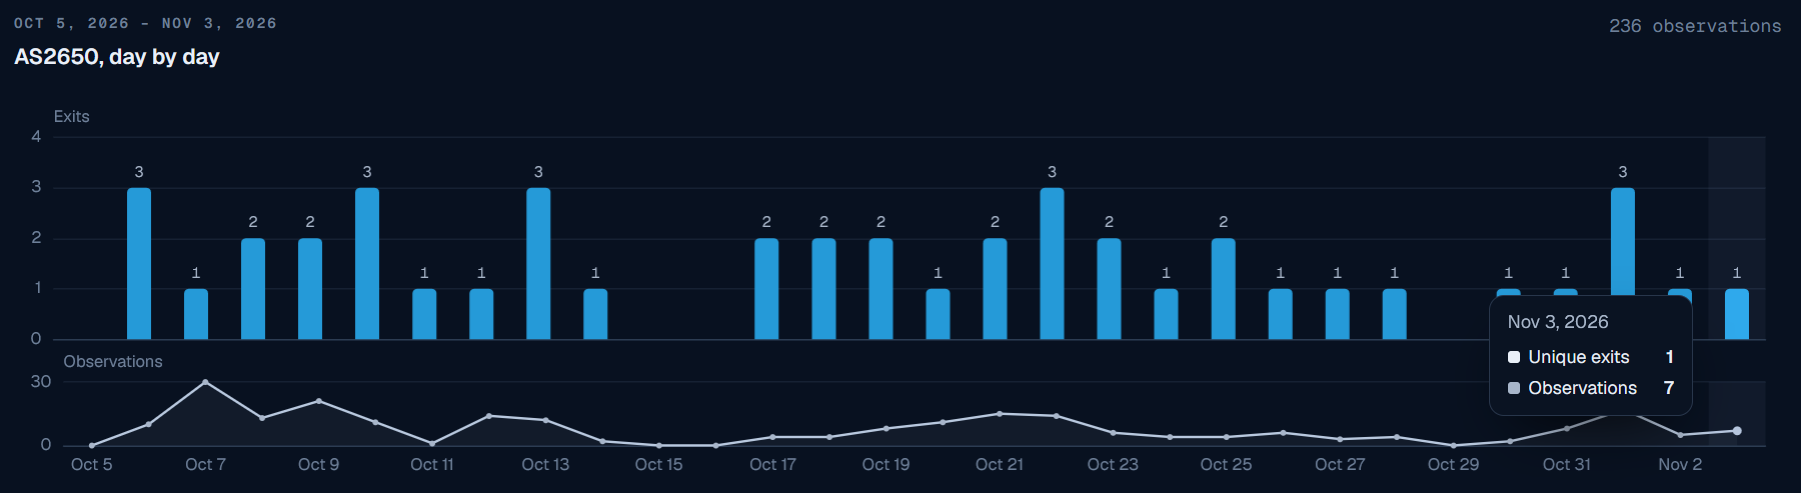
Residential proxy exit activity was detected originating from the White House network between October 5 and November 3, 2026, according to data from the Residential Proxy Observatory. The activity, identified on the AS2650 network registered to the Executive Office of the President, suggests that devices within this high-security environment may be participating in anonymized traffic rerouting services.
Layer3 Intel, which launched its Residential Proxy Observatory earlier this week to monitor global anonymized network activity, identified the presence of these proxies through its enumeration pipeline. The findings indicate that the White House network served as an exit point for residential proxy traffic 236 separate times over the month-long observation period. This activity was not a continuous stream but was concentrated across six specific addresses and occurred on 26 of the 30 days monitored.
Residential Proxy Services Compromise AS2650 Network
Residential proxies function by rerouting internet traffic through the IP addresses of everyday consumer devices, such as home routers or personal computers, to mask the true origin of the request. While the use of these services is not inherently illegal, they are frequently utilized by threat actors to facilitate illicit operations, including malware distribution and denial-of-service attacks. In this instance, 28 different residential proxy services were able to exit through the White House’s network, Layer3 Intel reported.
To validate the findings, researchers cross-referenced the identified addresses with other detection services, including Spur and Synthient. These third-party platforms independently confirmed that the addresses in question functioned as residential proxy exits. The researchers noted that they did not target the White House network specifically; rather, the connection was discovered by chance while requesting global rotating access through public proxy services.
‼️ The White House network was acting as a residential proxy, letting paid strangers' traffic exit through it 236 times in a month, threat-intel firm Layer3 Intel says. Layer3 bought a few dollars of proxy access and saw traffic come out of 6 addresses registered to the… pic.twitter.com/PMZOW5YjM7
Patterns in Traffic Timing Suggest Individual Device Infection
Roughly half of the proxy exits occurred between 5 p.m. and midnight Eastern Time, with almost no activity recorded in the early morning hours. This temporal pattern deviates from the behavior of a public guest Wi-Fi network and instead suggests the activity of a specific person on the network whose device has likely been compromised by a proxy SDK.
Software Development Kits (SDKs) used by proxy providers can sometimes be poorly secured, creating vulnerabilities that allow for lateral movement within a network. This mechanism mirrors how previous botnets have expanded. For example, researchers at Synthient documented the Kimwolf botnet, which reached at least 2 million devices—primarily Android units with exposed ADB services—by using residential proxy networks. If the SDKs active on the White House network possess similar flaws, they could theoretically allow external actors to reach internal systems.
Global Ubiquity of Anonymized Network Traffic
The detection in the White House is part of a trend of residential proxy saturation across even the most isolated regions of the planet. The Observatory’s data reveals that no location is immune to this type of internet interference.
- Saint Helena: The researchers recorded 413 addresses and over 32,000 observations on this remote South Atlantic territory, split between the local provider, Sure Saint Helena, and Starlink.
- Antarctica: Three observations were recorded originating from a Cloudflare WARP address pointing to McMurdo Station.
- Enterprise Environments: Recent research from Infoblox corroborates that residential proxies are widespread throughout various enterprise networks, not just isolated government agencies.
The Technical Mechanics of Proxy Exits
| Metric | Observed Data (Oct 5 – Nov 3, 2026) |
|---|---|
| Total Exit Events | 236 |
| Unique IP Addresses | 6 |
| Active Days | 26 of 30 |
While Layer3 Intel has indicated a willingness to share raw logs with relevant agencies, the specific identities of the devices or the individuals using them remain unknown.
More on White House
The post is accurate. Layer3 Intel documented 236 residential proxy exits from 6 AS2650 (Executive Office of the President) addresses via 28 commercial services over Oct 5–Nov 3 2026 (26 of 30 days). Founder Sergiy Usatyuk confirmed to RuntimeWire they have not notified the White…
