
Addressing organizational context gaps highlighted in its 2026 Developer Survey—which found that 75% of developers waste more than 5 hours weekly hunting for information and 79% uncover vital context only after beginning a task—Stack Overflow rolled out its October Stack Internal and Stack Internal Community updates.
Scopes and Permission-Governed Context Layers
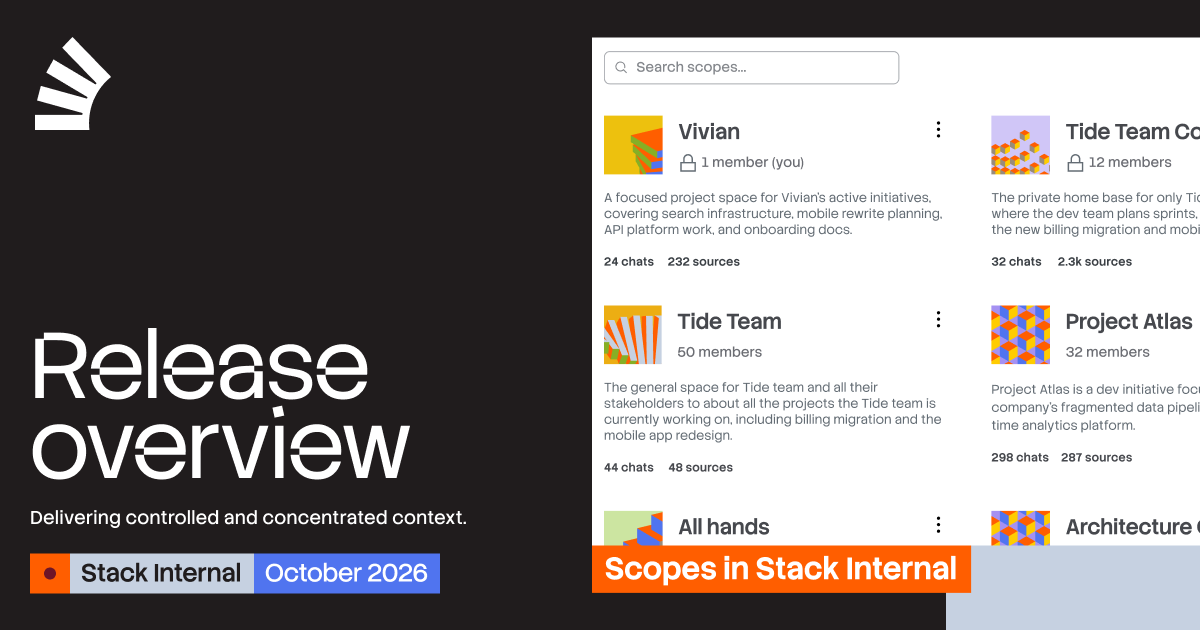
The update introduces Scopes within Stack Internal. These context layers let organizations shape information into permission-governed spaces. Scopes control what knowledge is included and who can utilize it, delivering concentrated context to humans and AI agents without noise or unauthorized exposure. Users can fluidly switch contexts between different project, team, or department spaces. Alternatively, teams can direct an AI agent to query a specific Scope via the Model Context Protocol (MCP) server.
Stack Internal and Stack Internal Community are engineered to operate in tandem. Stack Internal Community acts as a human-verified system of record, while Stack Internal pushes that truth into daily developer workflows and AI toolchains. This creates a compounding, self-sustaining memory layer across the enterprise.
Automated GitHub Ingestion and Access Controls
To turn static repositories into active enterprise memory, the company announced an out-of-the-box GitHub connector. The connector ingests engineering knowledge living in organization-owned code discussions—including issues, pull requests, and repository documentation—directly into Stack Internal’s verified knowledge layer. It automatically captures high-signal engineering decisions and documentation without manual upkeep.
Importantly, the GitHub connector maintains pre-existing GitHub access controls for both human users and AI agents by enforcing source-level permissions.
Service Accounts and Secure Application Workflows
Organization workspaces can now connect applications, MCP clients, and automated workflows to Stack Internal using service accounts instead of relying on personal tokens or shared user accounts. Applications receive a stable identity and standard OAuth flow for developers, whereas security teams are provided with easily manageable lifecycles.
By tying each service account to a single workspace equipped with distinct credentials, permissions, and an auditable identity, you can securely integrate Stack knowledge into your existing enterprise-agent workflows.
Validation APIs and Moderator Tools
Stack Internal integrates a Subject Matter Expert (SME) validation flow directly into the web user interface via a new Reviews feature. This allows users to validate questions from others in their workspace in a centralized location.
To keep connected sources updated as institutional knowledge evolves, the platform introduces a validation API endpoint. Custom integrations can be built by teams to track Stack Internal validations, sort by chosen timeframes, sources, or topics, and seamlessly push that refreshed, verified knowledge back into external platforms like Confluence or Stack Internal Community.
Simultaneously, Stack Internal Community receives updates including animated GIFs in Q&A posts and articles, clear reasoning for obsolete posts, attribution for unaccepted answers, streamlined moderator management with targeted announcements, granular SME controls, search activity exports, and a History page tracking site-setting changes.
