
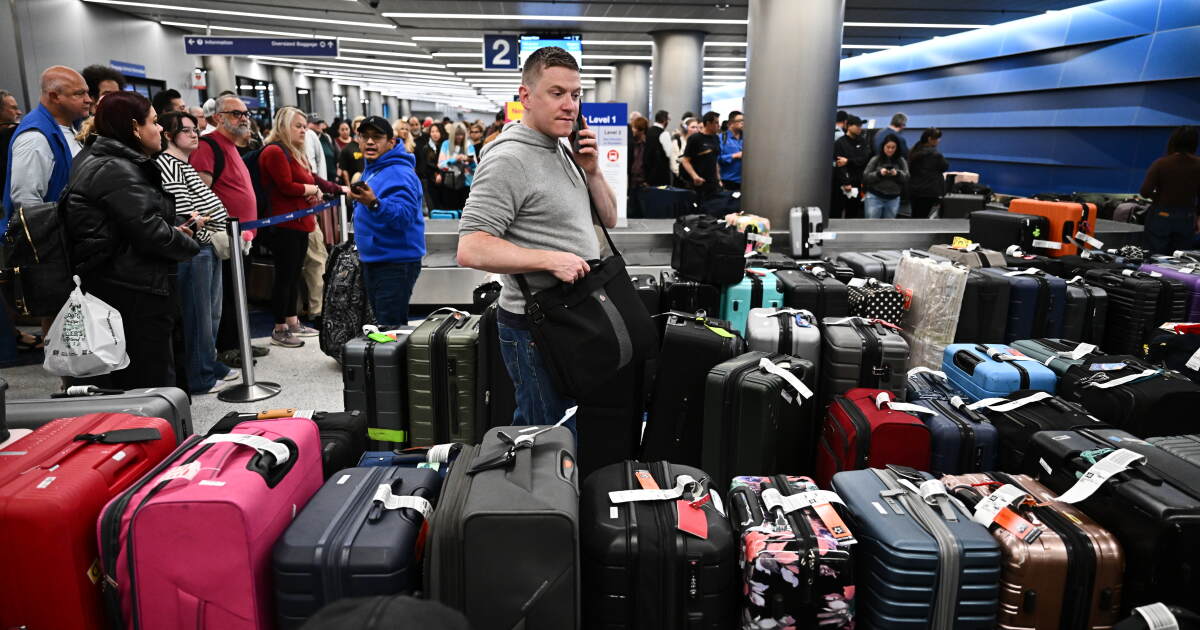
Nationwide flights ground to a halt after a cascade of technology failures disrupted crucial United States infrastructure, prompting officials to clarify that the outages were not the result of a coordinated attack.
The technological instability began with emails across the Microsoft system failing, followed by disruptions to banking services at JPMorgan Chase on Monday. Major outages subsequently afflicted Apple and Marriott International on Tuesday, alongside the U.S. National Security Agency’s highly classified internal communications network.
Government officials sought to minimize the severity of the week’s events, with President Donald Trump telling reporters in Manila that the incidents were not a cyberattack or a coordinated action by a nation state. Jay Clayton, Director of National Intelligence, addressed the disruption from Washington, attributing the outages to the widespread patching and upgrading of aging, insecure digital systems by numerous companies and institutions.
However, experts in cyber policy questioned the characterization of the failures. Marcus Rogers, director of the Cyber Forensics Lab at Purdue Polytechnic Institute, described the situation as a “muddy picture,” noting that six incidents across different infrastructures starts to become “alarming.” Rogers argued that if the problems were caused by minor human errors or failure to upgrade infrastructure, it made critical U.S. systems a potentially bigger target for bad actors.
T.J. Marlin, founder and CEO of Guardrail Technologies, said the odds were extremely low that so many essential systems would break down by chance within such a brief window. He argued the pattern pointed toward a shared underlying cause, such as a common vendor, update or dependency (such as AI).
Senate Intelligence Committee ranking member Mark Warner, D-Va., said that AI is transforming the cyber security landscape by making it possible to identify vulnerabilities across enormous numbers of systems at unprecedented speed, creating pressure on companies and government agencies to patch those vulnerabilities immediately, often all at once, putting strain on systems that weren’t built to handle that pace of change.
Herbert Lin, a senior research scholar at Stanford University’s Center for International Security and Cooperation and a fellow in Cyber Policy and Security at the Hoover Institution, raised doubts about whether a single actor was responsible for the failures. He said that while it seems very unlikely, the possibility of a shared cause could not be ruled out.
According to the FBI, malicious cyber actors have been using the open-source, large language model-driven ARTEX platform to automate cyber intrusions globally since at least August 2026. Google also warned that the era of autonomous attacks has arrived, noting that bad actors are using autonomous LLM frameworks to continuously scan software updates and build attacks without human involvement.
The failures have prompted lawmakers to demand immediate briefings.
Rep. Mike Lawler (R-N.Y.) called on the administration to brief Congress on the exact nature of the problem to facilitate an all-of-government response.
Experts warn that the reliance on complex, interconnected information systems creates inherent risk. Lin suggested that as a consumer, one should have cash on hand and emergency water.
In response to the ongoing chaos, California Governor Gavin Newsom said that the situation requires “mature leadership” and requires someone who takes responsibility.
More on United States
Director of National Intelligence Jay Clayton: "This is not a cyberattack and this is not a coordinated action by a nation state" pic.twitter.com/SK49eeGtJH
Given today’s cyberattack, coupled with the FAA ground-stops, banking failures, and Microsoft outage, it’s imperative the administration immediately brief Congress on the exact nature of the problem, so that we can have an all of government response. While some of this may be… https://t.co/J2f1J0dgqO
