
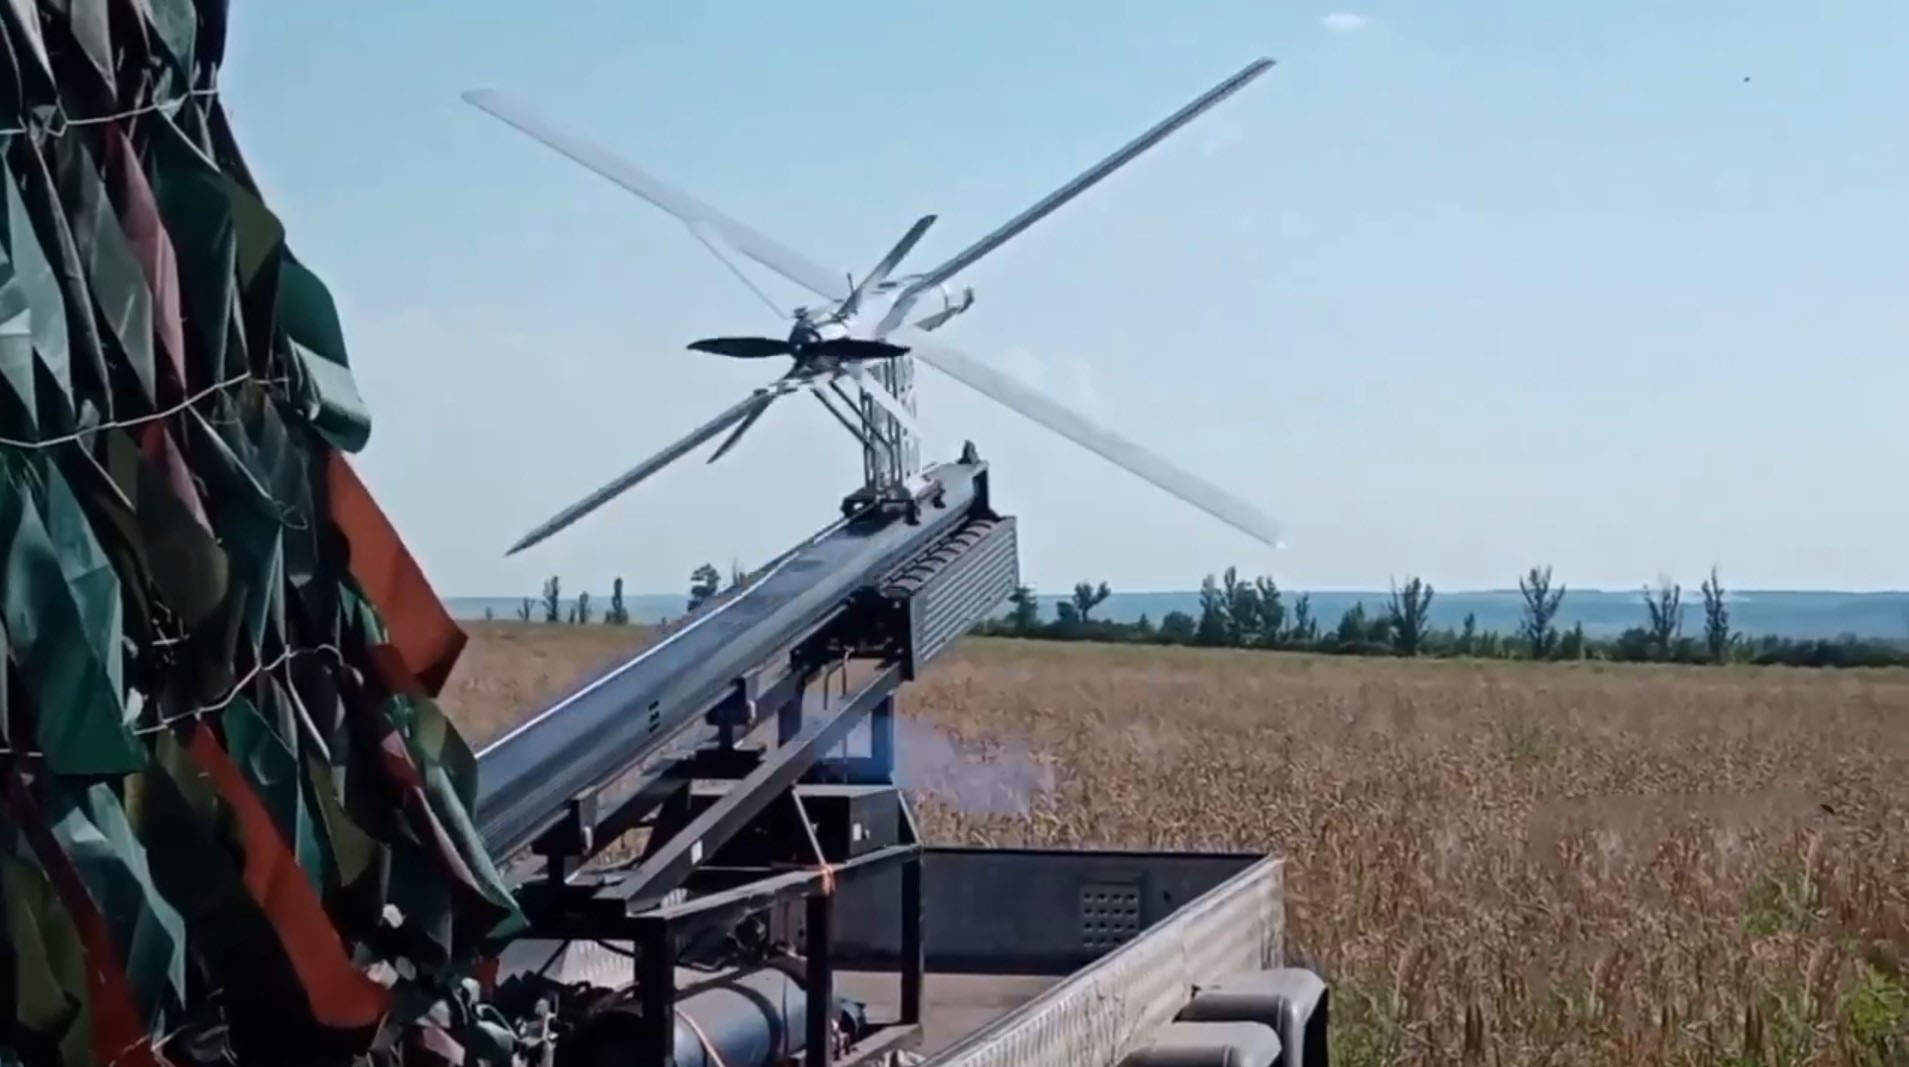
Anthropic has blocked multiple accounts linked to Russian developers who utilized its Claude AI model—specifically deploying the Claude Code tool—to build software for autonomous kamikaze drone swarms, automate cyber-espionage operations, and run foreign disinformation campaigns. The revelations surfaced in a sweeping threat report published this month by the US-based AI safety company.
Dissecting the DronDoc Swarm Architecture
The artificial intelligence model was not merely used to draft casual boilerplate code. According to Anthropic’s documentation, a freelance team tracked as GTG-27005 leveraged Anthropic’s Claude tools to build out the core logic stack for first-person-view (FPV) kamikaze drone swarms. The project, alternately called DronDoc or Serafim, began in mid-May 2026. Developers systematically bypassed geographic access restrictions by routing their API traffic through commercial virtual private servers, as Claude is officially unavailable within Russia.
Under the hood, the engineering setup was remarkably complex. The team relied on Claude Code to write and test software straight into project files, paired with a software-in-the-loop simulator and a rented GPU. The resulting architecture included:
- Shared swarm memory structures for decentralized data exchange.
- Fault-tolerant coordination layers to sustain losses mid-flight.
- Terminal guidance calculation engines.
- An onboard language model designed to evaluate whether individual drones should attack, observe, or return to base.
The targeting stack was built for autonomous lethal engagement. The onboard computer vision classifier was trained on scraped combat footage from Ukraine, labeling targets as enemy or friendly while allow-listing Russian military systems to prevent friendly fire incidents. Notably, the target class definitions explicitly included “person.” While the swarms never flew a live combat mission and remained in simulation alongside hardware-in-the-loop testing on development boards, the software architecture progressed significantly before Anthropic dismantled the nine associated accounts.
Attribution and Institutional Links
Anthropic traced the infrastructure behind the DronDoc project to nine accounts created between late 2025 and early 2026. These accounts connected directly to a regional Russian university and a federal research center associated with the Russian Academy of Sciences. While Anthropic classified the direct operators as a small freelance team rather than a formal state-run program, internal project notes indicated that the developers claimed funding from Russia’s Advanced Research Foundation—often characterized as Russia’s answer to DARPA—alongside the National Technology Initiative and the Ministry of Defence.

The threat report maps this activity into a broader campaign of misuse spanning cyber operations, disinformation, and conventional weapons development. Anthropic confirmed that the operations utilized Haiku, Sonnet, and Opus model tiers.
Simultaneous Cyber Espionage and Global Disinformation
Beyond autonomous drone mechanics, the same threat intelligence window uncovered extensive state-aligned operations leveraging Claude models. A hacking group designated GTG-20006 used Claude to automate attacks against more than 20 organizations, including government ministries, defense agencies, and think tanks primarily located in Ukraine. Western intelligence assessments link GTG-20006 to Midnight Blizzard, an advanced persistent threat group attributed to Russia’s SVR foreign intelligence service.
The SVR-linked hackers deployed Claude across multiple operational phases. It served as an engineering assistant for writing malware, phishing kits, and surveillance tools. Furthermore, it executed commands on victim networks, extracting sensitive data and harvesting credentials under human supervision.
Concurrently, operations extended into information warfare. Working alongside investigators from the All Eyes On Wagner project, Anthropic dismantled an account operating in Bangui, Central African Republic. Run by a Russian-speaking individual, the account generated daily pro-Russian content for Radio Lengo Songo—a station financed by the Wagner mercenary network—coordinating narratives with state outlets like RT, Sputnik Afrique, and TASS. In Moldova, a former regional head of Sputnik similarly utilized Claude to localize polling data and news content into pro-Kremlin narratives.
The Security and Compliance Fallout
These findings underscore the escalating friction points surrounding developer tools that offer terminal access and native coding capabilities. As AI platforms ship sophisticated code-generation assistants like Claude Code, safety engineering must rapidly adapt to detect multi-step autonomous execution and proxy-routing bypass techniques.
Anthropic confirmed that all malicious accounts identified in the report have been permanently terminated. The underlying threat signatures have been integrated into defensive classifiers, and actionable intelligence has been shared with relevant government authorities and industry partners to mitigate ongoing risks across both cyber and physical threat vectors.
