
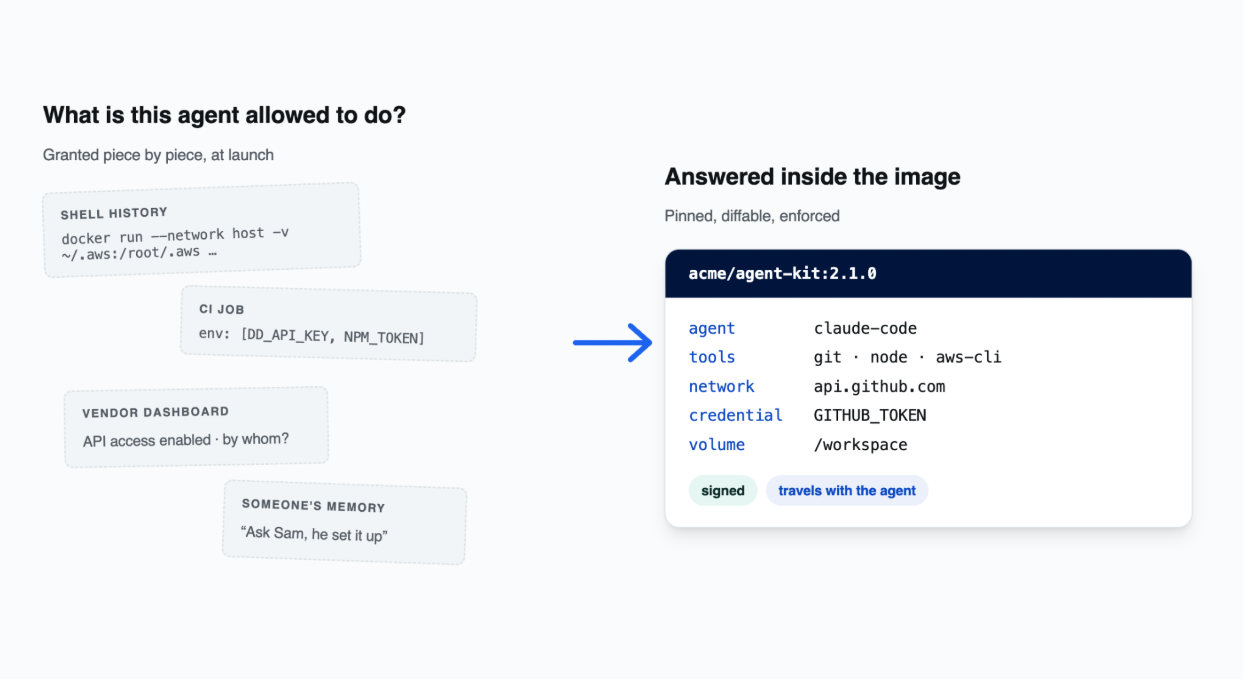
Docker has published the Sandbox Kit Spec under the Apache 2.0 license and committed to contributing the open specification to the Cloud Native Computing Foundation for neutral governance. The move aims to solve AI agent fragmentation by making permissions, tools, and guardrails portable across different runtimes via standard OCI container images.
Packaging AI Agents and Guardrails Into OCI Images
Historically, Open Container Initiative (OCI) images tell a runtime how to build and start software. However, they lack any mechanism to dictate network hosts, credentials, or filesystem volumes that an application can access. For standard web services, launch configurations handled these restrictions through docker run flags, a Compose file, a CI job, or an onboarding doc because the software’s behavior remained relatively static.
AI agents break this architectural paradigm. Tools like Claude Code and Codex dynamically decide which packages to install, which APIs to query, and how to manipulate their runtime environment. Over time, an agent’s granted access spreads across shell history, dashboards, and memory, making it impossible to audit.
The newly published Sandbox Kit Spec solves this by using an existing extension point within OCI specifications. It embeds a typed list of requested resources directly into the image manifest using OCI annotations. Because a Kit is an ordinary OCI image, developers can build, push, pull, sign, and scan the artifact using existing container tooling without modifying registries or scanning tools.
CNCF Governance Ensures Broad Industry Compatibility for Kits
Kits originated as a feature of Docker Sandboxes, a product that runs agents inside isolated microVMs. Under the new specification, any compliant runtime can read and enforce the attached capability limits. Docker Sandboxes is the first runtime that enforces it, but CNCF governance ensures broader industry compatibility.
Chris Aniszczyk, CTO of the CNCF, emphasized the strategic necessity of standards in preventing ecosystem fragmentation. “Standards are what let an ecosystem move fast without fragmenting, and few companies understand that better than Docker,” Aniszczyk stated. “By delivering Sandbox Kits as standard OCI images, Docker is giving the industry an open, repeatable way to package an AI agent, its tools, and its guardrails as one artifact.”
Initial platform support spans multiple sectors of enterprise infrastructure. Kits for tools published by AWS, Box, Datadog, Dynatrace, JFrog, NanoClaw, OpenClaw, Palo Alto Networks, and Snyk are currently available. This allows database vendors and observability platforms to bundle pre-configured Kits that connect agents to their services under recommended permission scopes.
Enterprise Teams Can Audit AI Agent Privilege Requests
As Docker transitions the specification to the Cloud Native Computing Foundation, enterprise teams can integrate Kit verification. When an AI agent requests expanded privileges in a new release, the modification appears as added lines, allowing reviewers to audit or reject the change before deployment.
Developers and platform engineers can examine the specification, capability pages, and a worked tour of a real Kit directly via the public repository at docker/sandbox-kit-spec.
