
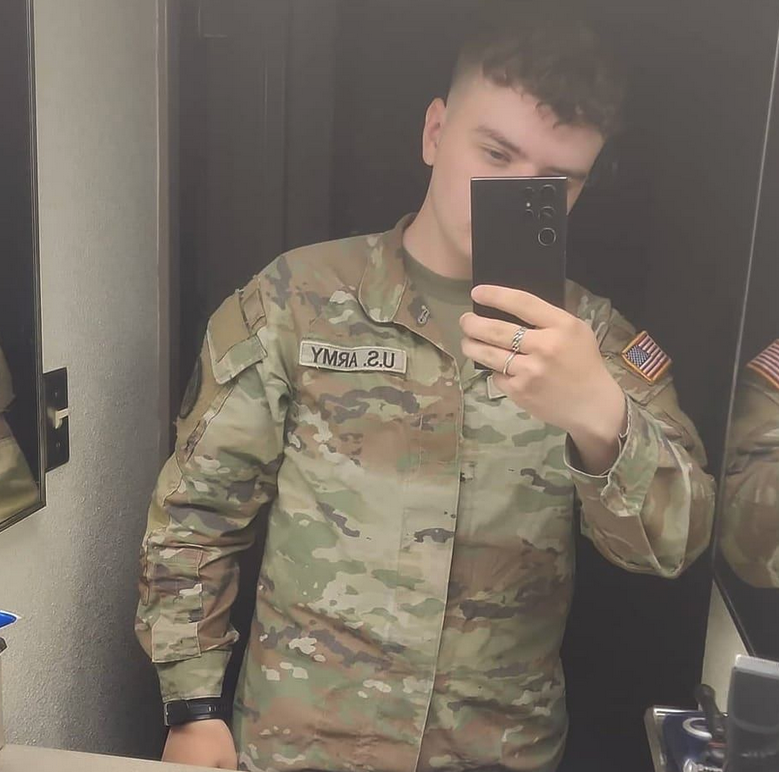
Cameron John Wagenius, a 22-year-old U.S. Army soldier stationed in South Korea, was sentenced to 70 months in federal prison and ordered to pay $294,978 in restitution for hacking telecommunications firms, extorting companies, and stealing metadata belonging to over 100 million AT&T customers.
The Persona of Kiberphant0m and the Snowflake Exploits
Operating under the cybercriminal handle “Kiberphant0m,” Wagenius used exposed credentials belonging to large customers of cloud data storage service Snowflake. Because these accounts failed to enforce multi-factor authentication, the soldier and his co-conspirators downloaded massive volumes of enterprise data. Snowflake has since mandated multi-factor authentication across all accounts.
In October 2024, Kiberphant0m boasted on illicit forums that he had exfiltrated call and text metadata—including source numbers, destination numbers, timestamps, and call durations—for tens of millions of AT&T customers. krebsonsecurity.com reported that the hacker claimed responsibility for breaches across more than a dozen global telecommunications providers, targeting assets like Verizon’s Push-to-Talk infrastructure and publicly extorting the companies under the threat of publishing the raw records.
Unraveling the Insider Threat in South Korea
The investigation accelerated in late November 2025 when KrebsOnSecurity published warnings indicating that Kiberphant0m was likely an active-duty U.S. soldier stationed on the Korean peninsula. Less than a month after that identification, law enforcement arrested Wagenius, hitting him with two separate federal indictments.
Paul Russell, resident agent in charge at the Defense Criminal Investigative Service, highlighted the atypical nature of the case. “We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data,” Russell stated, noting that the insider threat galvanized the FBI, the Army Criminal Investigative Division, and the U.S. Secret Service into immediate action.
Co-Conspirators and National Security Extortion Tactics
Prosecutors detailed a network of digital accomplices assisting Wagenius in his extortion schemes. Kenneth Schuchman, a 28-year-old from Vancouver, Washington, joined the operation with an established cybercriminal record; Schuchman previously pleaded guilty in 2019 to operating the Satori botnet, which hijacked Internet-of-Things devices for large-scale distributed denial-of-service attacks.
Prison AI Queries and the Bureau of Prisons Breach Attempt
Federal court filings submitted on September 19 revealed that Wagenius continued his technical probes while incarcerated and awaiting sentencing. Using other inmates’ email systems, he prompted commercial artificial intelligence tools to bypass standard safety guardrails via prompt injection techniques.

According to Bureau of Prisons records cited by prosecutors, Wagenius asked an AI to generate real-world working scripts without omitted code for Windows 10 Enterprise privilege escalation vulnerabilities, and queried CVE-2023-45208, a command injection flaw affecting D-Link networking devices.
Despite the immense volume of data exfiltrated from corporate giants, prosecutors noted that Wagenius’s monetization efforts were largely ineffective, yielding an estimated total of roughly $1,500 from selling stolen records.
