
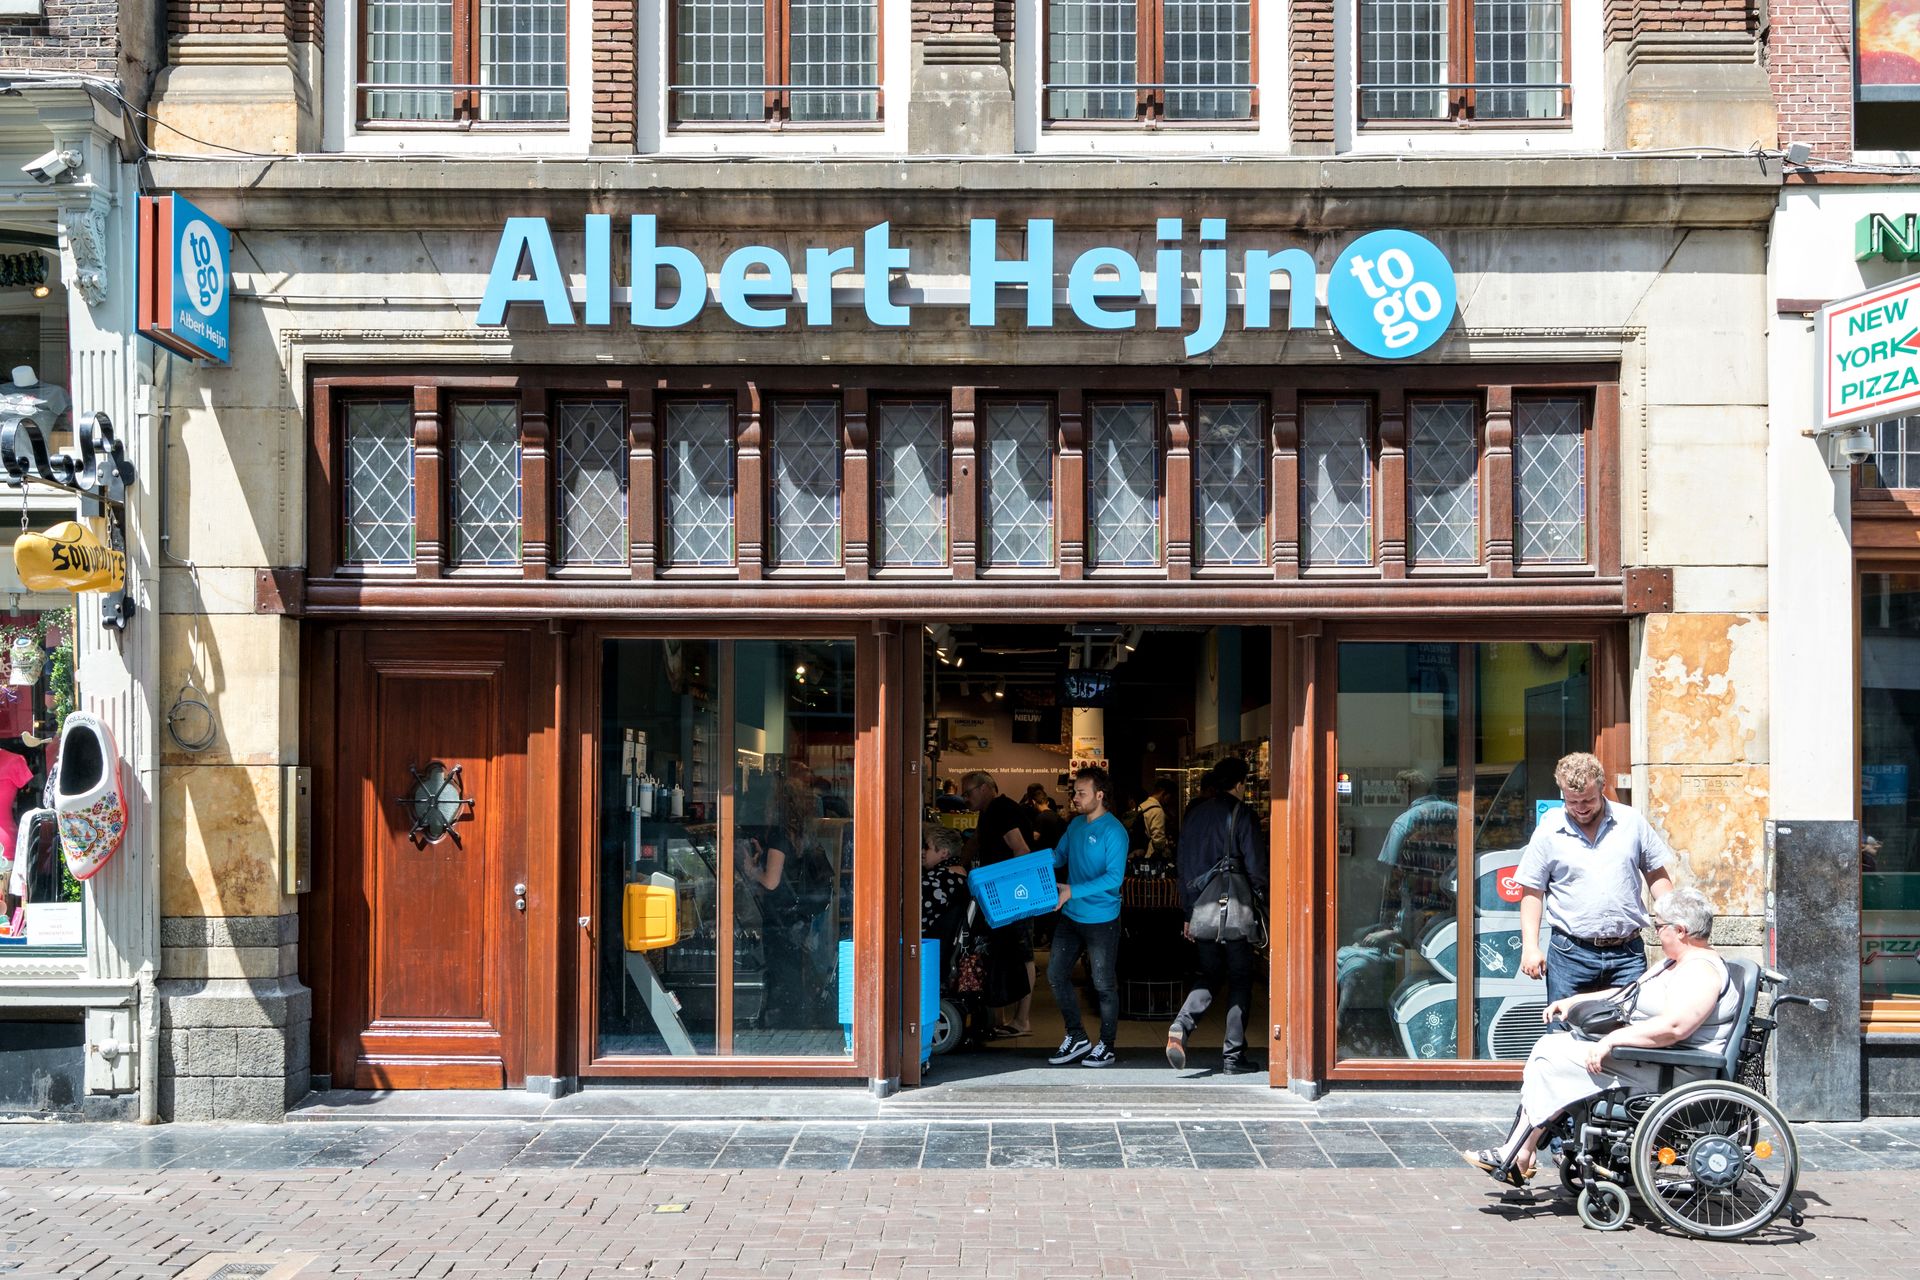
In October 2026, a cyberattack struck supermarket chains, forcing remote systems to spike refrigeration temperatures up to 50 and 80 degrees Celsius.
The Bottom Line
- Operational Impact: Hundreds of retail locations across France experienced forced mass-defrost cycles, compromising cold-chain compliance and forcing immediate inventory write-offs.
- Cross-Border Infrastructure: Intelligence tracking confirmed that server nodes in Poland were co-opted to route the intrusions.
- Regulatory Response: National prosecutors and specialized cybercrime units launched coordinated investigations to identify the threat actors behind the industrial refrigeration override.
Cross-Border Infrastructure and the Dutch Attack Vector
When the security breach hit the Dutch market over the weekend preceding October 13, 2026, initial operational anomalies targeted major retail brands. According to Interia, public broadcaster reports confirmed that server infrastructure stationed in Poland served as the operational backbone utilized during the cyberattack on Albert Heijn, the largest supermarket network in the Netherlands.
The incident disrupted core digital environments and web interfaces, prompting immediate defensive isolation protocols by IT security teams. While Dutch systems moved swiftly to contain the network intrusion, parallel disruptions unfolded on a massive industrial scale across neighboring European markets.
Thermal Sabotage in French Supermarket Coolers
The scale of the physical damage became apparent as retail executives assessed ruined inventory. TVN24 reported that approximately 700 supermarkets in France faced deliberate thermal manipulation of their commercial refrigeration systems. Unidentified actors infiltrated remote management software, disabling standard cooling controls and pushing internal unit temperatures to extremes.
Thierry Cotillard of the Les Mousquetaires group noted that attackers remotely activated rapid-defrost cycles, elevating unit temperatures to 50 degrees Celsius. Meanwhile, Business Insider Polska noted that specific store locations reported temperatures soaring as high as 80 degrees Celsius, resulting in melted equipment seals and total inventory loss.
| Retail Network / Entity | Impacted Locations | Reported Operational Damage |
|---|---|---|
| Coopérative U | 80 supermarkets | Massive stock disposal; severe cold-chain disruption |
| Intermarché & Netto | 150 to 200 stores | Equipment deformation; inventory written off in millions of euros |
| Albert Heijn (Netherlands) | Unspecified scale | IT infrastructure targeted via proxy servers |
Vulnerabilities in Industrial Control Systems
Technical assessments point directly to remote management interfaces connected to legacy industrial hardware. According to TVN24 and Business Insider Polska, the compromised refrigeration control systems were manufactured by Danish firm Danfoss. Reuters reported that the cyberattack affected Copeland and Dixell systems.
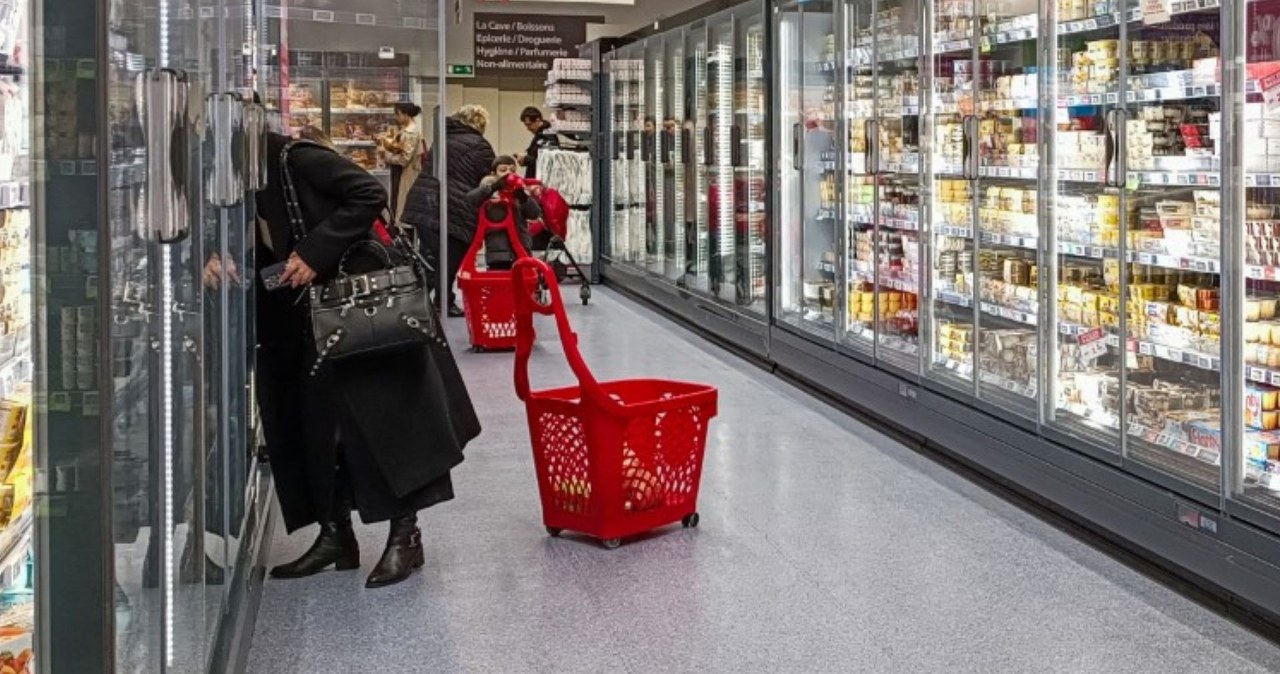
Manufacturer statements indicated that the affected units largely comprised legacy hardware lines that had reached the end of their designated support lifecycle, lacking contemporary firmware security patches. Cybersecurity experts emphasized that industrial internet-of-things integration leaves operational technology exposed when remote monitoring tools lack multi-layered authentication.
Financial Exposure and Ongoing Judicial Inquiries
Economic losses across the affected retail groups are mounting rapidly. Industry leaders estimate total damages in France alone will reach tens of millions of euros once complete inventory write-offs and equipment replacements are calculated. Dominique Schelcher of Coopérative U, characterized the event on RTL radio as an unprecedented and deeply serious assault on national food security.
In response, the Paris public prosecutor’s office initiated a formal ex officio judicial investigation on October 12, 2026. The probe is led by specialized cybercrime divisions and the national cyberthreat agency, which continues to coordinate with international European counterparts to trace the origin of the proxy routing through Poland.
Related reading
- Nuon Medical debuted facial and scalp care devices at In-Cosmetics Global
- Plan in Decades, Not Quarters: HamiltonJet Keeps Leadership in Family
- 1,590 French Danfoss Systems Were Still Online Hours After the Hack (daybreakwire.com)
- U.S.Next Cyberattack Disrupts Mississippi Websites and Email (news-usa.today)
