
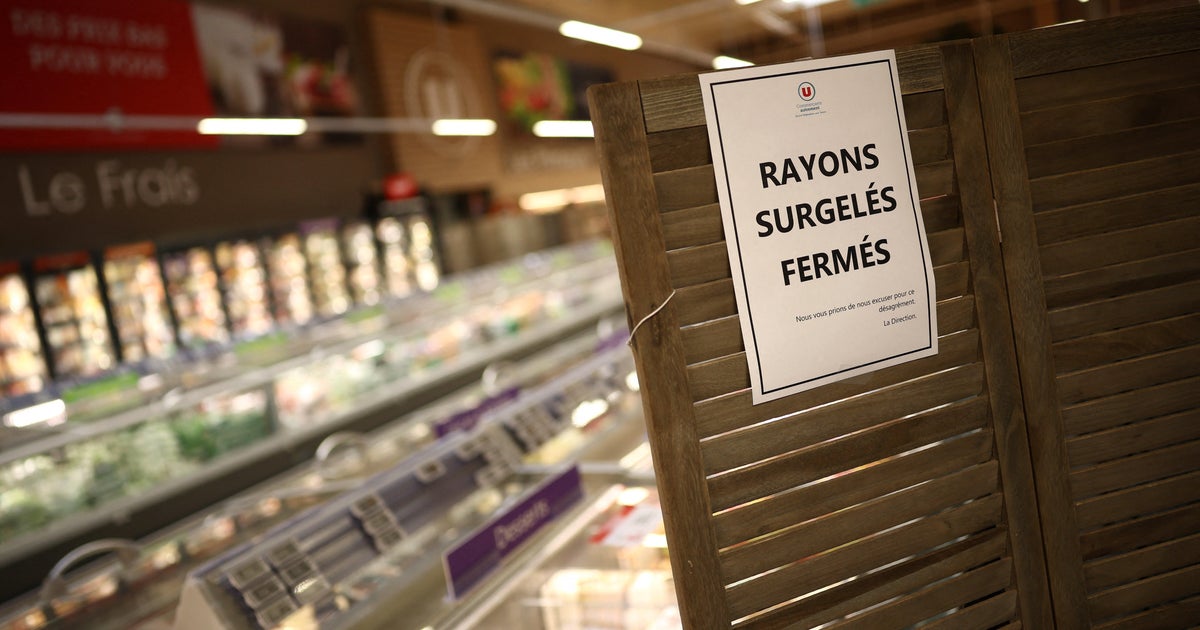
A coordinated cyberattack struck major French supermarket chains on Monday, forcibly driving up refrigerator temperatures in hundreds of stores, spoiling fresh and frozen inventories, and triggering fires in multiple locations. Top retailers E. Leclerc, Intermarché, and Cooperative U confirmed to Agence France-Presse that their facilities were targeted in what Cooperative U’s chief executive described as an “unprecedented” assault.
The breach exploited software vulnerabilities linked to Danish industrial equipment manufacturer Danfoss. According to BFM TV, malicious actors “managed to remotely trigger the forced defrosting of the refrigeration systems in numerous stores.” The resulting thermal spikes destroyed perishable stocks and forced operators to discard entire aisles of chilled and frozen goods.
Scale of the Damage Across Retail Networks
The operational disruption hit hundreds of storefronts across France, exposing the deep vulnerabilities of digitally connected commercial hardware. Intermarché reported that at least 300 of its locations and Netto brand discount shops were compromised. Leclerc sustained operational disruptions across several stores after its refrigeration equipment suppliers were breached.
Carrefour announced that 80 of its supermarkets were affected by the intrusion, though the vast majority of its 6,000-store domestic footprint remained online, according to Reuters reporting. Beyond French borders, Dutch supermarket operator Ahold Delhaize disclosed a parallel security issue disrupting its corporate network, with customer-facing applications warning shoppers that home delivery services were temporarily offline due to a cybersecurity incident.
Vulnerable Legacy Hardware and Vendor Responses
Investigators tracing the intrusion point toward refrigeration control systems manufactured by Danfoss. In a public statement, Danfoss confirmed that the targeted units were primarily “legacy” products—specifically its AK-SM800 and AK-SC355 fridge regulator systems—which no longer receive active software or security updates. The company noted that a version of the AK-SM800 series was running outdated firmware, and stated it had long advised supermarket operators to upgrade their infrastructure.

Antoine Hautin of the cybersecurity consultancy Almond told AFP that the simultaneous disruption of hundreds of units points to a high level of sophistication among the attackers.
Government Probes and International Warnings
The Paris prosecutor’s office confirmed that a formal criminal investigation has been launched into the large-scale cyberattack, tasked with identifying victims, quantifying food waste losses, and investigating the origin of the fires sparked inside affected stores. A person close to Sebastien Lecornu stated that France’s national cybersecurity agency has already identified the software vulnerability tied to the Danish vendor and established contact with the manufacturer.
The incident has amplified anxieties across Europe regarding hybrid warfare and the targeting of critical civilian infrastructure. EU food and agriculture commissioner Christophe Hansen condemned the incident on X, writing that food security demands heightened vigilance and describing the deliberate exploitation of the food supply chain as a stark new reality.
