
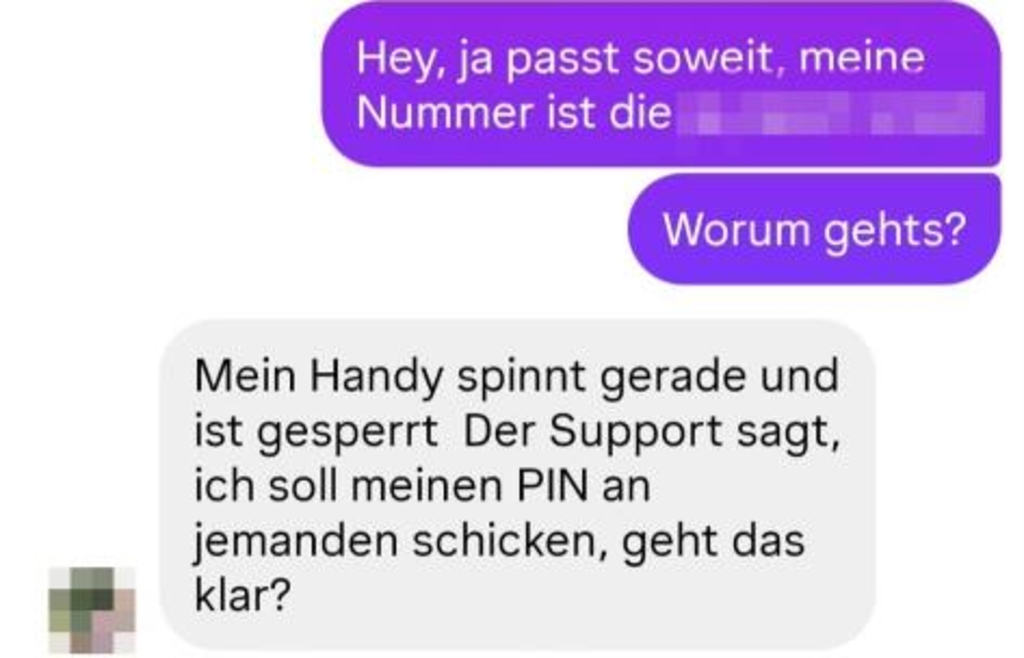
A 27-year-old resident of Burghausen in the Altötting district recently lost a high three-digit euro sum to a calculated social engineering scam executed entirely through Instagram. While the underlying deceptive playbook has circulated across broader digital platforms for several years, this marks the first documented case of its kind within the regional jurisdiction.
The Anatomy of a Compromised Social Feed
Modern credential harvesting exploits have evolved past blunt-force phishing vectors. Instead, they rely heavily on trusted-network manipulation within platforms like Meta’s Instagram. Attackers typically compromise an established user profile first. From there, they leverage the existing social graph to distribute malicious links, fabricated investment traps, or urgent financial pleas to unsuspecting followers who lower their guard due to the familiar sender identity.
In the Altötting case, the victim interacted with what appeared to be a legitimate contact whose account had already fallen under unauthorized control. The perpetrators capitalized on this trusted environment by deploying tactics designed to induce panic or urgency. This rapid manipulation of trust allowed the bad actors to siphon a substantial three-digit euro amount before the account holder could flag the unauthorized access.
Shifting Realities for Local Law Enforcement
Defensive Protocols and Prevention Measures
Security guidelines for high-risk social media users now demand the deployment of robust defensive measures:
- Enforce strict multi-factor authentication (MFA) utilizing hardware security keys or authenticator apps rather than vulnerable SMS-based verification.
- Treat unexpected financial requests or link-sharing prompts from known contacts with extreme skepticism until identity verification occurs via an out-of-band channel like a direct phone call.
- Regularly audit active login sessions and authorized third-party application permissions within account security settings.
The Burden on Consumer Digital Hygiene
The Burghausen incident highlights a persistent vulnerability in consumer-facing SaaS architectures: identity validation on social networks remains fundamentally fragile. As threat actors automate credential stuffing and session hijacking via modern API exploits, individual users bear an asymmetric burden of security upkeep. For regional law enforcement, rising digital crime rates demand a pivot toward proactive public awareness campaigns to combat threats that bypass geographic borders with a single tap.
