

PentestCode, a newly deployed AI agent, is automating penetration testing by integrating 18 specialized cybersecurity tools into a single autonomous workflow. Launched for beta testing this week, the platform aims to identify network vulnerabilities at machine speed, shifting the paradigm from manual red-teaming to continuous, high-velocity automated security assessments.
The Architectural Shift Toward Autonomous Red-Teaming
The cybersecurity industry has long struggled with the “dwell time” problem—the gap between a vulnerability appearing and a human analyst identifying it. PentestCode attempts to close this window by orchestrating 18 distinct security tools into a unified, AI-driven pipeline. Unlike static vulnerability scanners that rely on pre-defined signatures, this agent utilizes large language model (LLM) reasoning to interpret output from reconnaissance, exploitation, and post-exploitation modules.
At its core, the system acts as an orchestrator. It manages state machines for each tool, parsing JSON and raw text outputs from traditional utilities like Nmap for network mapping and specialized fuzzers for protocol analysis. By chaining these inputs, the agent can pivot from an initial service discovery to a simulated exploit attempt without human intervention. This is not merely script automation; it is an attempt to replicate the decision-making logic of a junior penetration tester.
Technical Integration and API Orchestration
PentestCode’s efficiency relies on its ability to handle asynchronous data streams. In a typical enterprise environment, the overhead of managing 18 tools simultaneously would result in significant latency and resource contention. The agent mitigates this by leveraging containerized micro-services, likely utilizing Docker or Kubernetes clusters to isolate the compute-heavy tasks of vulnerability scanning.
The agent’s API-first approach allows it to integrate with existing CI/CD pipelines. This is the “Shift Left” philosophy taken to its logical extreme. By embedding these tests directly into the deployment process, developers can identify insecure dependencies or misconfigured cloud buckets before code reaches production. The architecture supports:
- Automated Reconnaissance: Passive and active scanning using integrated OSINT tools.
- Exploit Chaining: The ability to combine multiple low-severity vulnerabilities to achieve a high-impact outcome.
- Reporting Automation: Translating raw CVE data into actionable, risk-prioritized remediation tickets.
The 30-Second Verdict: Why This Matters for Enterprise IT
For CISOs and security operations centers (SOCs), the primary value proposition is the reduction of manual fatigue. However, the reliance on AI for penetration testing introduces a new attack vector: adversarial manipulation of the AI agent itself. If the agent can be tricked into ignoring specific subnets or misinterpreting a critical vulnerability as a false positive, the security posture could be compromised from the inside out.
As noted by cybersecurity researchers in recent discussions on GitHub’s open-source security repositories, the move toward automation is inevitable, yet it mandates a “human-in-the-loop” requirement for high-stakes environments. You cannot automate the accountability that comes with a signed audit.
Ecosystem Bridging and the Future of AI Security
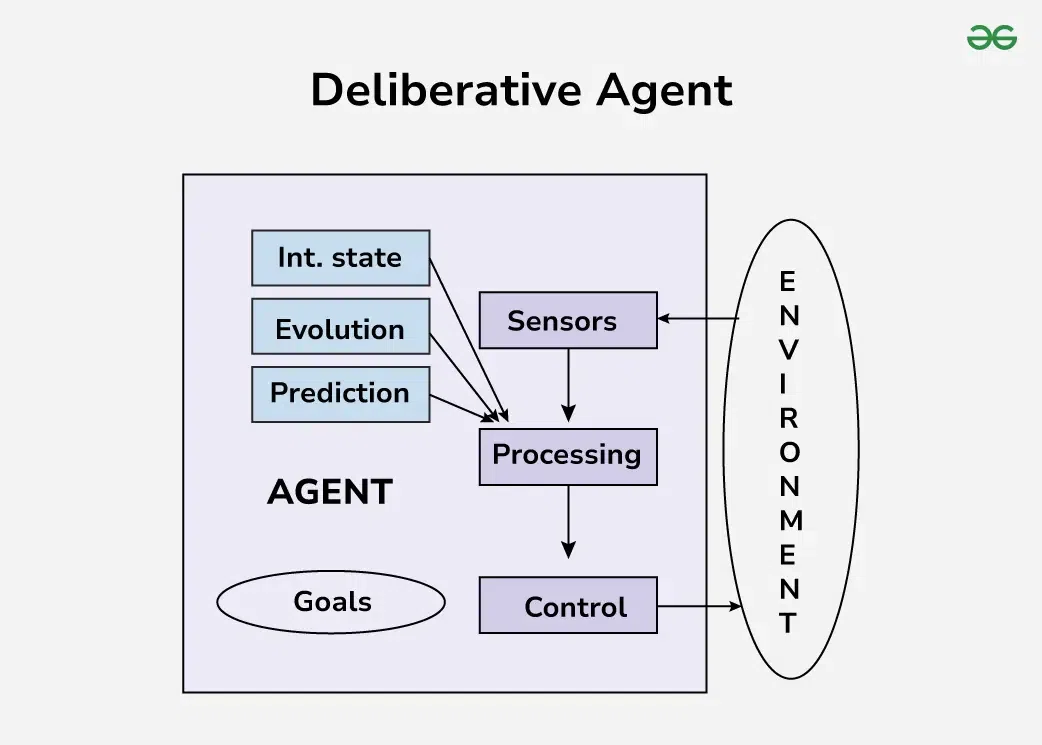
PentestCode enters a crowded market dominated by established players like Rapid7 and Tenable. The differentiator here is the agentic nature of the software. While legacy tools are often “passive observers,” PentestCode is an “active participant.” This shift aligns with the broader trend of autonomous agents, similar to the developments seen in IEEE-documented research on self-healing network architectures.
The industry is currently divided on the efficacy of these tools. Some analysts argue that AI-driven testing will force attackers to evolve, moving away from known CVEs toward novel, logic-based exploits that AI agents are currently ill-equipped to detect. Others, such as those monitoring the National Vulnerability Database, suggest that the sheer volume of known vulnerabilities makes automation the only viable path to maintaining a baseline level of security.
What remains to be seen is how the agent handles the “false positive” noise. In a large-scale network, 18 tools running concurrently will generate a deluge of alerts. If the LLM backend cannot effectively prune these, the agent will quickly become a nuisance rather than an asset. The success of PentestCode will ultimately be measured not by the number of tools it runs, but by the signal-to-noise ratio of its final intelligence reports.
We are witnessing the transition of security from a static checklist to a dynamic, living process. If this beta proves stable, the next six months will likely see a surge in similar “agentic” security tools, effectively turning the network perimeter into a constantly shifting, self-defending entity.
