
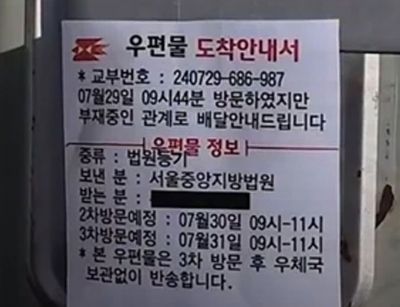
The “letter phishing” scam resurfaced on the 26th, targeting residents with counterfeit postal arrival notices left on front doors and in mailboxes. Unlike traditional voice phishing where fraudsters initiate contact, this scheme forces victims to make the initial call, leading to severe financial and personal data exposure.
Fantasy & Market Impact
- Victims face immediate financial exposure, including demands for cash, culture gift certificates, and virtual assets.
- Fraudsters frequently escalate tactics by forcing targets to install malicious applications or endure prolonged video calls under false pretenses.
- Security protocols demand verifying postal notices directly through official agency hotlines rather than dialing numbers printed on suspicious slips.
The Mechanics of the Counterfeit Notice
The scam relies on a carefully engineered psychological trap. Fraudsters affix forged documents mimicking actual postal service arrival notices onto apartment doors or residential mailboxes. The notice explicitly claims that a registered mail delivery failed, providing a fake contact number disguised as a delivery worker’s direct line.
Once the victim dials the number, the operation scales rapidly. The initial responder poses as a delivery agent and transfers the call to an accomplice impersonating law enforcement or prosecutors. The caller then asserts that the victim’s identity is tied to active criminal investigations or illicit funds, applying immense pressure to comply with remote investigative demands.
Escalation Tactics and Personal Data Theft
The operation goes beyond simple monetary extortion. Recent cases highlighted by the Korean National Police Agency demonstrate that perpetrators use messaging platforms like Telegram to enforce prolonged video calls. In specific instances, victims were coerced into undergoing fraudulent remote body checks involving personal video recordings.
Criminal syndicates have also instructed targets to purchase separate mobile devices incapable of blocking malicious applications. This maneuver ensures continuous access to the victim’s device, enabling the extraction of sensitive personal data stored locally.
| Incident Vector | Primary Method | Associated Risk |
|---|---|---|
| Notice Distribution | Forged postal slips on front doors | Direct victim-initiated calls |
| Impersonation | Delivery workers to prosecutors | Coercive criminal investigations |
| Digital Compromise | Malicious apps and separate devices | Data extraction and video extortion |
Historical Precedent and Official Countermeasures
This method is not entirely novel; law enforcement agencies have tracked similar iterations since 2023. A notable breakthrough occurred in Gyeongju, where authorities uncovered an operation that distributed 1,538 forged notices. Police successfully tracked and extradited the primary overseas mastermind from China to face domestic prosecution.
Law enforcement officials reiterate that official agencies never request application installations, personal data, or monetary transfers via telephone calls. Residents discovering suspicious delivery notices are advised to bypass the printed numbers entirely, verifying the status of any alleged parcel directly through official postal customer service channels or by contacting the police at 112 and the Financial Supervisory Service at 1332.
Immediate Response Protocols for Compromised Devices
Swift action remains essential if an individual interacts with these fraudulent networks. Victims who have already installed malicious software must sever network connectivity immediately by blocking mobile device communication. Contacting financial institutions to request payment suspensions can prevent unauthorized asset transfers.
