
Major domestic South Korean commercial banks are pushing to fully computerize their tens of thousands of IT assets following a security breach that exposed vulnerabilities in asset visibility.
Managing Tens of Thousands of Software and Hardware Assets
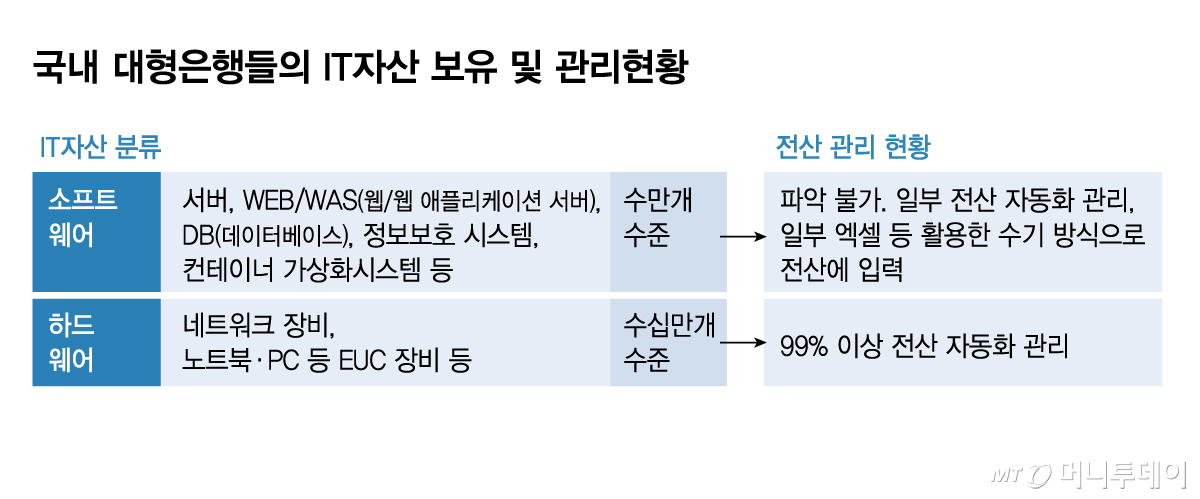
Large banks in South Korea manage up to tens of thousands of IT assets, including servers, web servers, Web Application Servers (WAS), databases, information security systems, and container virtualization systems. However, technical limitations in existing asset management systems often force financial institutions to rely partly on manual record-keeping through tools like Excel.
The total volume of these assets cannot be tracked with exact precision because financial institutions have spent a long time developing and operating complex core systems. Business units and software developers frequently spin up new programs or establish external access points to meet operational demands as they arise.
Assets are introduced, modified, and decommissioned constantly, making comprehensive inventory tracking difficult. Consequently, some system records go missing or end up manually typed into spreadsheets rather than unified asset databases. Financial authorities determined that a recent hacking incident occurred largely because security teams failed to maintain complete visibility over the existence, configuration, and security posture of every program running on their networks.
Implementing Software Bill of Materials Across Major Banks
Financial regulators are placing specific emphasis on the adoption of a Software Bill of Materials (SBOM) to catalog every component inside enterprise applications. An SBOM inventories open-source components, software libraries, version numbers, and the precise interdependencies connecting them.
Adoption across the major commercial banking sector remains fragmented. Among the top four banks—KB Kookmin, Shinhan, Hana, and Woori—only one has deployed an SBOM across a portion of its systems. The remaining three institutions are still in the preliminary planning or rollout stages of adoption.
Banking industry stakeholders acknowledge that mandatory identification and centralized management of IT assets will reduce security blind spots. Enhanced visibility allows security teams to identify vulnerabilities and prioritize patching cycles much faster than manual audits allow.
Discusses Security Risks and Logistical Hurdles in Asset Management
Centralizing all IT asset information into a single repository introduces new architectural risks, creating a potential single point of attack for threat actors. Analysts and industry insiders also debate the direct causal link between the recent hacking incident and poor asset tracking. The intrusion used an authentication-bypass vulnerability within a system that was already actively managed, rather than exploiting an uncataloged shadow asset.
Automating comprehensive inventory collection across legacy infrastructure presents significant logistical hurdles. A large bank official noted that few vendors currently offer solutions capable of automating 100% of asset management under existing technical constraints, meaning full computerization will require a substantial timeline. The official emphasized that regulatory mandates should be preceded by explicitly designating internal asset owners and scoping manageable asset boundaries to prevent operational confusion during deployment.
