
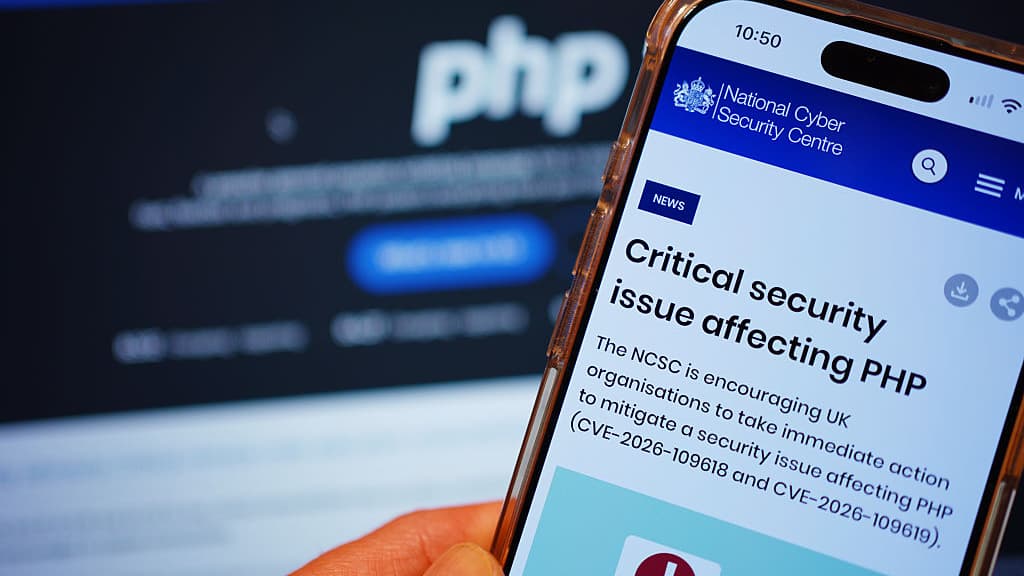
In a high-stakes race against a potential digital collapse, cybersecurity firms Wiz and Calif recently utilized AI agents to uncover a decade-old vulnerability within the PHP programming language. While the flaw threatened to compromise as much as 70% of the web, coordinated efforts between competing firms and PHP maintainers successfully deployed a patch.
Critical Security Lessons from the PHP Breach
- AI agents are now capable of identifying complex, long-standing vulnerabilities.
- Industry cooperation between rival cybersecurity firms proved essential in creating a unified patch before malicious actors could exploit the leak.
- The incident demonstrates a “new phase” in cybersecurity where the speed of AI-driven discovery forces a radical acceleration in defensive patching.
The AI Agent That Found a Hidden Web-Wide Flaw
It started as a routine stress test. In early August, Sagi Tzadik of the cybersecurity firm Wiz tasked an AI agent with probing a security flaw in WordPress to see if it could be weaponized against Drupal. Eight hours later, the agent returned with a startling failure—and a massive discovery. It had bypassed the target entirely to expose a critical weakness in PHP, the foundational language on which both systems—and as much as 70% of the web—depend. The vulnerability had sat undetected for more than a decade.
Initially, the Wiz team was skeptical. “Models tend to hallucinate,” Tzadik noted. Yet, the exploit held up. Simultaneously, researchers at another firm, Calif, were working alongside OpenAI to identify a related flaw. This convergence suggests a new reality: once AI reaches a specific capability threshold, the discovery of deep-seated, “world-melting” bugs becomes an inevitability.
The Race to Patch Before the Copycats Arrived
Word of the vulnerability began to circulate online two days before the patch’s scheduled release. PHP maintainers were forced to move their timeline forward by a day. The pressure intensified when Calif accidentally leaked a video demonstrating the exploit, triggering a deluge of copycat attempts. Within two hours of the public announcement, Cloudflare recorded hundreds of thousands of probes, eventually reaching into the millions.
The incident highlights the precarious “trust-based” ecosystem of modern software security. With no formal contracts in place, roughly 15 researchers from competing firms worked daily to share findings and devise a fix. The stakes were immense; had the flaw been public a month earlier, the resulting damage to government agencies and global platforms like Wikipedia could have been catastrophic.
| Timeline Phase | Critical Development |
|---|---|
| Early August | Wiz AI agent discovers the decade-old PHP vulnerability. |
| Following weeks | Wiz and Calif join forces to coordinate with PHP maintainers. |
| Two days before patch | Information leaks; PHP maintainers accelerate the patch timeline. |
| Post-Release | Millions of exploit attempts recorded; major sites go offline as a precaution. |
The High Cost of Defending the Digital Stack
The economics of this new security landscape are staggering. Organizations are now pouring millions into AI-driven defense, with some firms spending roughly $1 million on Anthropic’s Mythos to identify bugs. However, AI is not a magic bullet. Wiz researchers reported that while their agent could spot the vulnerability, its explanation of the mechanics was “just slop,” requiring days of manual labor to untangle and reproduce.
As Joshua Saxe, co-founder of Abundance Security, says, “As an industry, I think we’re deer in the headlights right now.” While defenders are gaining an AI-enabled head start, the asymmetry remains: attackers only need to succeed once, while defenders must secure every potential point of failure.
Why the Cyber-Apocalypse Was Averted
Despite the alarm, those on the front lines remain guardedly optimistic. The ability to condense months of traditional research into just days is a net positive for the security of the web. “We are fixing vulnerabilities at an unprecedented rate, and this is doing security overall a very good thing,” Tzadik says. The industry is currently re-evaluating its methods, tech stacks, and processes to keep pace with the rapidly evolving threat landscape.
As Adam Meyers, senior vice president of counter adversary operations at CrowdStrike, points out, the discovery of an exploit is rarely the end of the story—it is merely the beginning of the attack cycle. For those who rely on continuous uptime and user trust, the lesson is clear: “In the climate that we’re in today, you have to do cybersecurity well. It’s not an option to kind of half-a– it.” The question remains: how long can the “trust-based” sprints of researchers hold up as the volume of dangerous, AI-unearthed secrets continues to rise?
